Cybersecurity News
Filters
Filtered by tag: dark web × Clear

Cybercriminals Are Selling Corporate Executives’ Social Security Numbers for Just 25 Cents
Matched: health
Rapid7 has tracked 476 compromised SSN records tied to 395 corporate executives on dark web marketplaces since early 2026, with records selling for as little as 25 cents. C-suite executives account for 44.6% of affected profiles. Three platforms — Xilo, Bankomat, and PeopleFinder — represent 81.5% of leaks, sourcing data from large breaches, infostealers, and phishing. Unlike passwords or cards, SSNs cannot be changed, making them permanently exploitable for fraud and impersonation schemes.
Are employees to blame for rise in insider access threats? This new study claims so
Flashpoint research found roughly 34 daily dark web posts related to insider threats between July 2025 and 2026, with July 2026 alone seeing 12,653 posts. Notably, 75% originated from insiders actively selling access rather than criminals recruiting them. Telecom, retail, and finance were primary targets. Flashpoint warns that as security software improves, attackers increasingly exploit employees, recommending organizations monitor dark web forums and encrypted platforms for credential trading.
No-Filter 'Kriminal' AI Platform Raises Cybercrime Concerns
Matched: cryptocurrency
A platform called "Kriminal" offers an AI service with no content restrictions, marketed toward cybercriminals. Accessible via cryptocurrency, it provides social engineering scripts, offensive hacking tools, and open-source intelligence scanning. Despite official terms prohibiting illegal use, researchers warn the guardrail-free system meaningfully lowers the barrier for cybercrime, enabling even unskilled actors to conduct sophisticated attacks.
Exclusive: 2019 allegedly hacks BestPriceTravel Australia
Matched: Australia
A threat actor has claimed responsibility for hacking BestPriceTravel Australia, listing the company on a dark web forum. The group, known as 2019, alleges it stole customer data from the online travel agency. The breach has not been independently verified, and it remains unclear how many customers may be affected or what type of data was compromised.
What Are Initial Access Brokers?
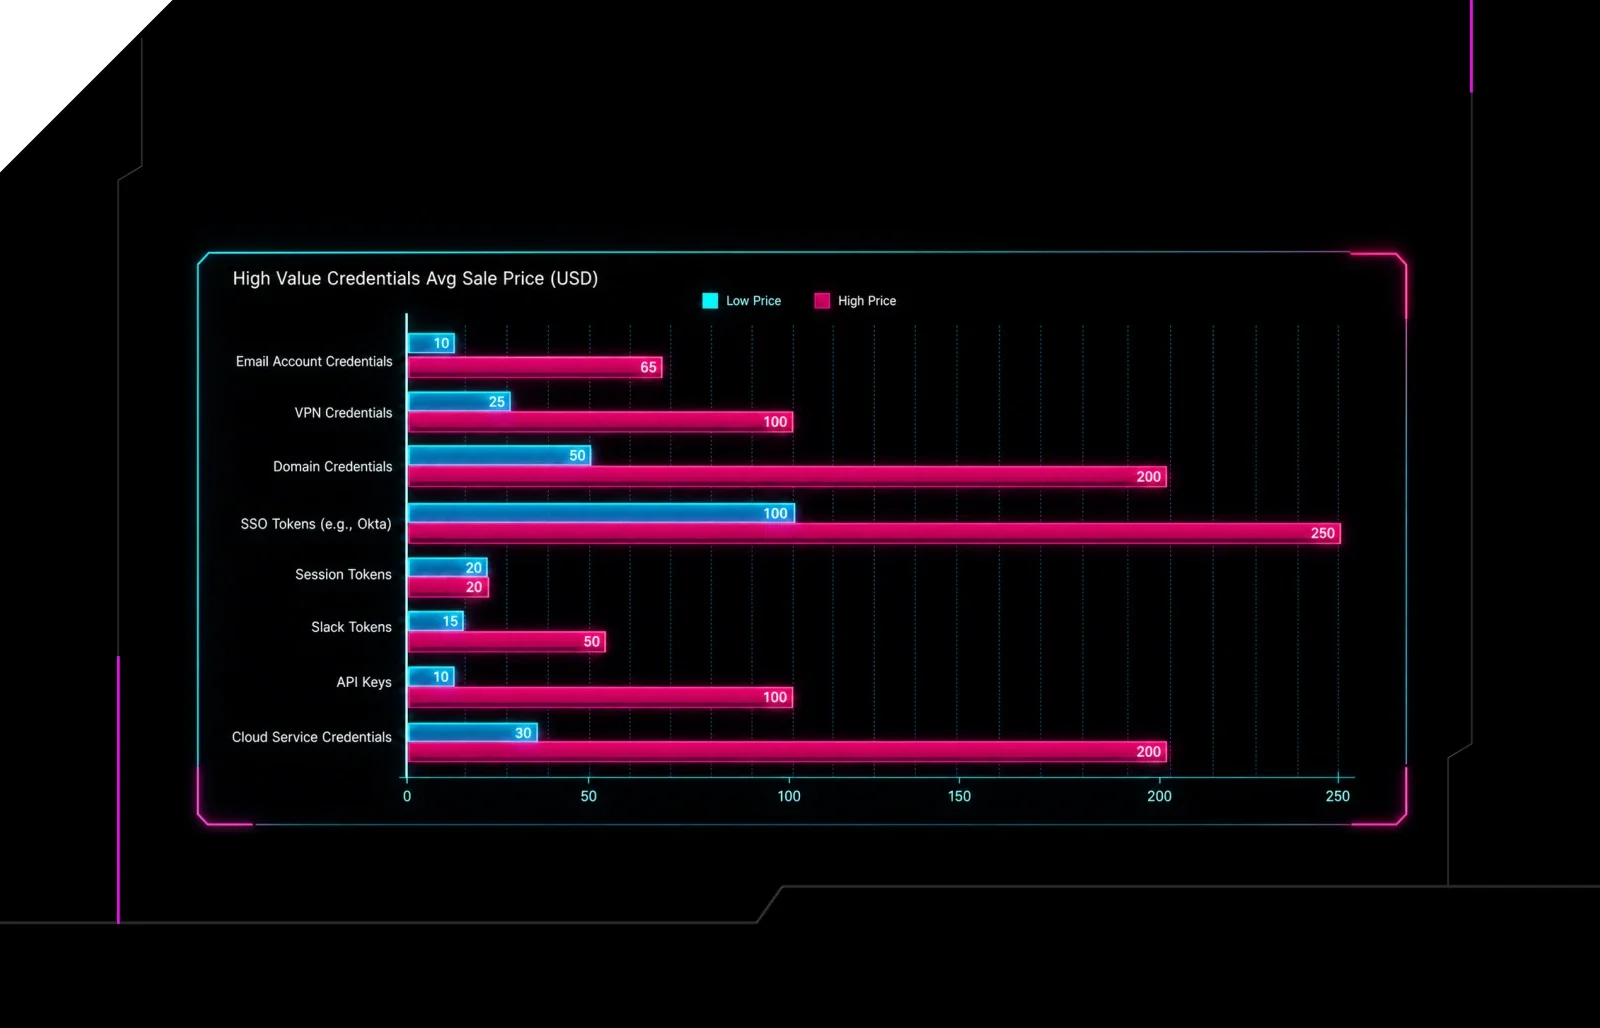
Initial access brokers are cybercriminals who specialize in breaking into corporate networks and selling that access to other attackers, such as ransomware groups, rather than exploiting it themselves. They typically gain entry through stolen credentials, phishing, or unpatched vulnerabilities. This division of labor has made cybercrime more efficient and increased the scale of attacks on businesses.