Cybersecurity News
Filters
Filtered by tag: data breach × Clear

Cybercriminals Are Selling Corporate Executives’ Social Security Numbers for Just 25 Cents
Matched: health
Rapid7 has tracked 476 compromised SSN records tied to 395 corporate executives on dark web marketplaces since early 2026, with records selling for as little as 25 cents. C-suite executives account for 44.6% of affected profiles. Three platforms — Xilo, Bankomat, and PeopleFinder — represent 81.5% of leaks, sourcing data from large breaches, infostealers, and phishing. Unlike passwords or cards, SSNs cannot be changed, making them permanently exploitable for fraud and impersonation schemes.
Boston Scientific says cyberattack is causing a ‘global disruption’ to medical device operations
Matched: medical
Boston Scientific confirmed a cyberattack causing global disruptions to IT systems and operations, filing an 8-K with the SEC. The incident has impacted order processing and shipping, with third-party cybersecurity experts brought in to assist. The attack type was not disclosed, though the disruption pattern suggests ransomware. No group has claimed responsibility, and no stolen data has been reported. Full restoration timeline remains unknown.
ShinyHunters hackers claim to have hit data center provider used by Microsoft and Meta
ShinyHunters claims to have breached CyrusOne, a major US data center operator serving Microsoft, Meta, and other large firms, demanding $13 million ransom. The alleged haul includes 12.9 million Salesforce records, 600GB of SharePoint data, employee PII, contracts, and facility diagrams including floor plans and access-control records. CyrusOne has not commented or engaged with attackers. Researchers warn the physical infrastructure data could enable real-world break-ins and sophisticated supply-chain attacks against CyrusOne's customers.
Are employees to blame for rise in insider access threats? This new study claims so
Flashpoint research found roughly 34 daily dark web posts related to insider threats between July 2025 and 2026, with July 2026 alone seeing 12,653 posts. Notably, 75% originated from insiders actively selling access rather than criminals recruiting them. Telecom, retail, and finance were primary targets. Flashpoint warns that as security software improves, attackers increasingly exploit employees, recommending organizations monitor dark web forums and encrypted platforms for credential trading.
Report: Australian CEOs face cyber accountability gap as AI accelerates attacks
Matched: Australia
More than half of Australian security professionals expect CEOs to lose their jobs following a major cyber breach, yet research highlights a significant gap between board-level accountability and actual operational preparedness. The disconnect is worsening as AI accelerates the pace and sophistication of attacks, raising concerns that leadership responsibility is outpacing organisations' real-world cyber defences.
Canadian SickKids hospital hit again by cyberattacks, more data stolen
Canada's SickKids pediatric hospital suffered a cyberattack exploiting a third-party software vulnerability, exposing personal data of current and former employees and job applicants. Clinical systems and patient records were unaffected. Those impacted are being offered 24 months of free credit monitoring. The hospital was previously hit by LockBit ransomware in late 2022, marking this its latest security incident.
Private equity giant Apollo confirms data breach saw personal info stolen
Apollo Global Management confirmed a cyberattack between July 6–10, 2026, in which a threat actor used social engineering to access its cloud environment. Stolen data included names, dates of birth, contact information, addresses, and Social Security numbers. Financial data was not compromised. Apollo notified authorities, engaged forensic experts, and is offering affected individuals two years of free identity protection. No group has claimed responsibility and the data has not appeared on the dark web.
Target may have suffered another damaging data leak as hackers claim 8.6GB haul
Hackers claim to have stolen 8.6GB of data from Target, potentially exposing customer and employee information. The threat actor posted the alleged haul online, though their credibility is uncertain due to a history of dubious claims. Target has not confirmed a breach. Cybersecurity researchers are investigating, urging caution given the source's track record of exaggerating or fabricating leaks.
Massive supply-chain attack sees terabytes of data belonging to some of the world’s biggest and most sensitive organizations leaked online
Hackers compromised a cybersecurity vendor's infrastructure, stole cryptographic signing keys for a widely used AI tool, and published a trojanized version under its legitimate name. The attack exposed terabytes of sensitive data from major organizations worldwide. The breach went undetected for an extended period, highlighting serious risks in software supply chains where a single compromised vendor can affect thousands of downstream users.
Healthtech firm CareCloud reveals March 2026 data breach impacted 3.7 million patients
Matched: health
Healthcare technology company CareCloud has disclosed a data breach that occurred in March 2026, affecting approximately 3.7 million patients. The company is notifying those impacted, though it has not revealed what specific types of patient information were compromised in the incident.
Over 9 million facial recognition images leaked in major breach at reverse image search and identity verification service
A facial recognition database belonging to ClarityCheck, a reverse image search and identity verification service, was left exposed, leaking over 9 million images. The breach was discovered by security researchers who notified the company, which subsequently secured the database. The incident raises serious privacy concerns given the sensitive biometric nature of the exposed data.
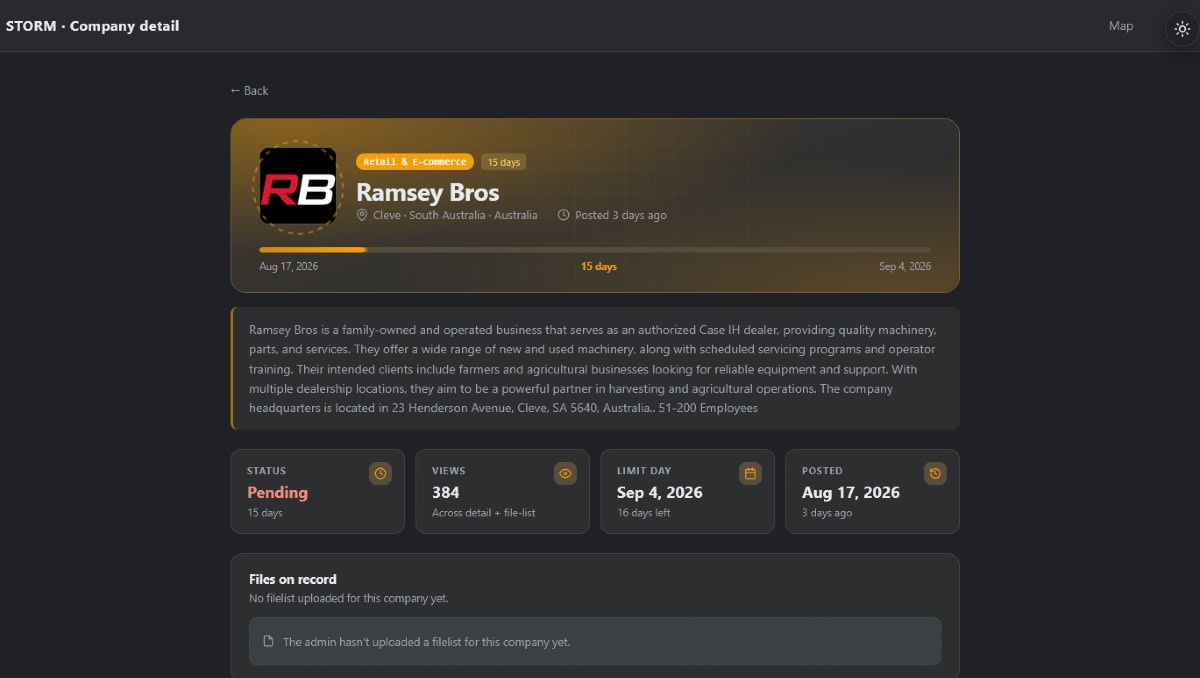
Exclusive: Ransomware newcomers list South Australia’s Ramsey Bros as hacking victim
Matched: Australia
Ransomware group Storm claims to have hacked Ramsey Bros, a South Australian farm machinery supplier. The group says it has published stolen data as proof, including alleged customer information and vehicle inspection records. Ramsey Bros has not yet publicly commented. Storm is considered a newcomer among ransomware groups, which typically steal and threaten to leak data to pressure victims into paying.
Faulty towers: Quest hotel chain discloses third-party customer data breach
Matched: Australia
Australian hotel apartment chain Quest has disclosed a data breach affecting customer information, including names, email addresses, and dates of birth. The breach originated from a third-party supplier rather than Quest's own systems. Affected customers have been notified and warned to remain vigilant against potential phishing attempts and scams that may exploit the compromised data.
SMEs aren’t too small to target for cybercriminals, they’re too exposed to ignore
Small and medium-sized businesses are increasingly targeted by cybercriminals due to weaker security defenses compared to larger organizations. Despite holding valuable data and often serving as supply chain entry points to bigger companies, many SMEs underestimate their risk exposure. Limited budgets and IT resources leave them vulnerable, making them attractive, easy targets rather than overlooked ones.
Loan company breach sees nearly 750,000 users have financial info, SSNs leaked
Heights Finance disclosed a data breach affecting nearly 750,000 customers after attackers compromised a cloud account. Stolen data includes Social Security numbers, bank account details, and other sensitive financial information. The loan company is notifying affected individuals and has urged them to monitor their accounts for suspicious activity.
Millions of stolen records allegedly dumped online by mystery "Hatman" hacker — McDonalds, Vodafone and more see Microsoft Azure records stolen
A hacker calling themselves "Hatman" has allegedly published millions of records stolen from companies including McDonald's and Vodafone, with the data appearing to originate from Microsoft Azure systems. Affected companies dispute the severity, saying the data is outdated and denying any breach of their own systems. The origin and full scope of the leak remain unclear.
Pokémon Center data breach exposes customer info, cancels some orders
Pokémon Center has disclosed a data breach affecting customer information, stemming from a cyberattack on logistics partner CEVA Logistics. As a result, some orders have been cancelled or delayed. The incident is part of a broader supply chain attack targeting CEVA Logistics, with Pokémon Center among several companies affected. Customers are advised to monitor their accounts for suspicious activity.
Exclusive: SIA Medical Centre confirms it is investigating cyber incident involving patient data
Matched: medical
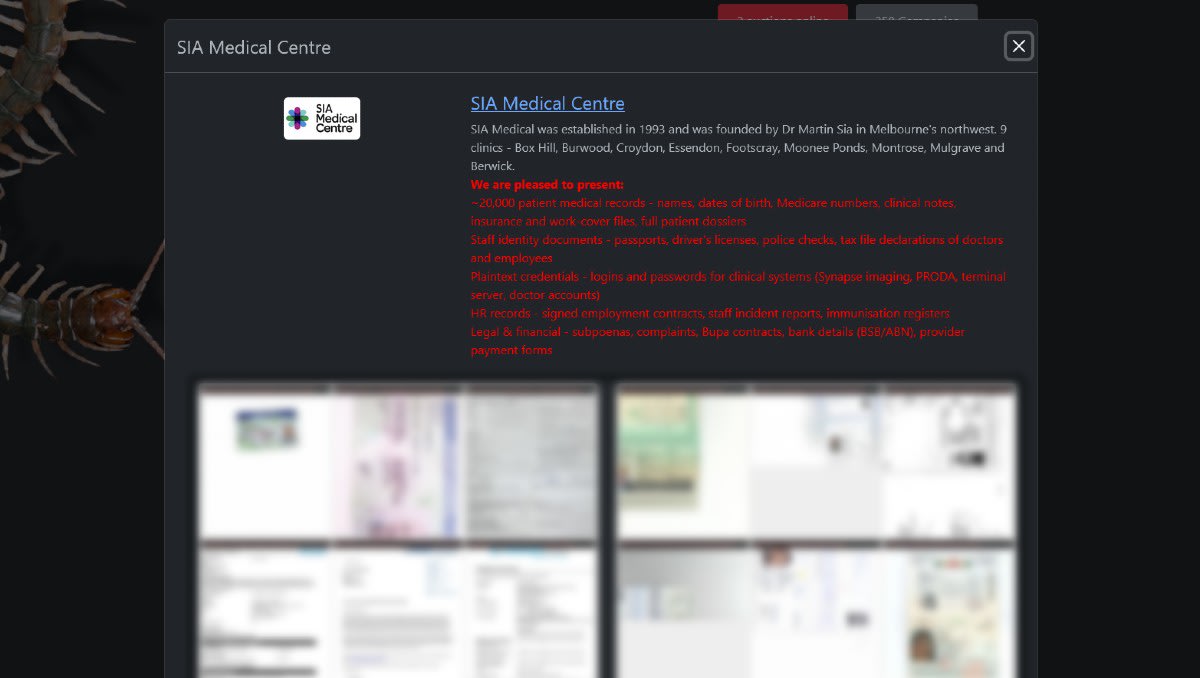
Victorian medical centre SIA Medical Centre is investigating a ransomware attack after the Rhysida cyber extortion group claimed to have obtained thousands of patient records. The centre confirmed it is responding to a cyber incident involving patient data. Rhysida, a known ransomware group, has listed the stolen data and is threatening to release it unless a ransom is paid.
17th August – Threat Intelligence Report
Colombia's Ministry of Justice suffered a ransomware attack disrupting technology infrastructure and public services tied to drug monitoring and legal processes, with officials confirming file compromise. Other notable incidents include additional breaches and cyberattacks detailed in Check Point Research's weekly Threat Intelligence Bulletin, covering top attacks, emerging vulnerabilities, and threat actor activity for the week of 17th August.
Exclusive: Aussie kidswear brand launches investigation following hacker claims
Matched: Australia
Australian kidswear retailer Aussie has launched an investigation after hackers claimed to have carried out a cyber attack against the company. The retailer confirmed it is aware of the claims and is looking into the incident. No further details about the nature of the breach or what data may have been compromised have been disclosed.