Cybersecurity News
Filters
Filtered by tag: enterprise security × Clear

AccuKnox Launches AgentZ to Help Enterprises Build, Run, and Govern AI Agents at Scale
Matched: health
AccuKnox has launched AgentZ, a platform for building, running, and governing AI agents across enterprise teams. It consolidates agents, execution environments, tools, workflows, permissions, and governance into one system. Key features include model-agnostic LLM support, sandboxed isolated execution, audit logs, multi-team access controls, and flexible SaaS, on-prem, or air-gapped deployment. A free hosted plan and open-source repository are available.
Are employees to blame for rise in insider access threats? This new study claims so
Flashpoint research found roughly 34 daily dark web posts related to insider threats between July 2025 and 2026, with July 2026 alone seeing 12,653 posts. Notably, 75% originated from insiders actively selling access rather than criminals recruiting them. Telecom, retail, and finance were primary targets. Flashpoint warns that as security software improves, attackers increasingly exploit employees, recommending organizations monitor dark web forums and encrypted platforms for credential trading.
No standing still: Zero Trust and cybersecurity
Cyberattacks are growing in speed and scale, costing businesses billions — recent incidents hit Jaguar Land Rover, WestJet, and Collins Aerospace. With public trust in data handling already low, companies need modernized security strategies. Zero Trust, built on "never trust, always verify," limits breach damage by confining access rather than relying on a single perimeter. Despite 96% of firms planning adoption, only 35% have implemented it, highlighting an urgent need for cross-industry action and consistent standards.
AI agents are inside the enterprise – are your security foundations ready for them?
As AI agents gain autonomous access to enterprise systems, data, and workflows, traditional software-level security measures are proving insufficient. Experts argue that organizations need hardware-level security foundations — including secure enclaves, trusted execution environments, and hardware attestation — to reliably verify agent identity, protect sensitive data, and prevent manipulation or compromise of increasingly autonomous AI systems.
Incident Response Plans: What to Include & Why They Matter
Organizations need incident response plans to minimize damage during cyberattacks. Key components include defined roles, communication protocols, detection and containment procedures, recovery steps, and post-incident analysis. Without a plan, response times slow and costs rise. Huntress helps by providing threat detection, guided remediation, and support that keeps businesses prepared before, during, and after security incidents.
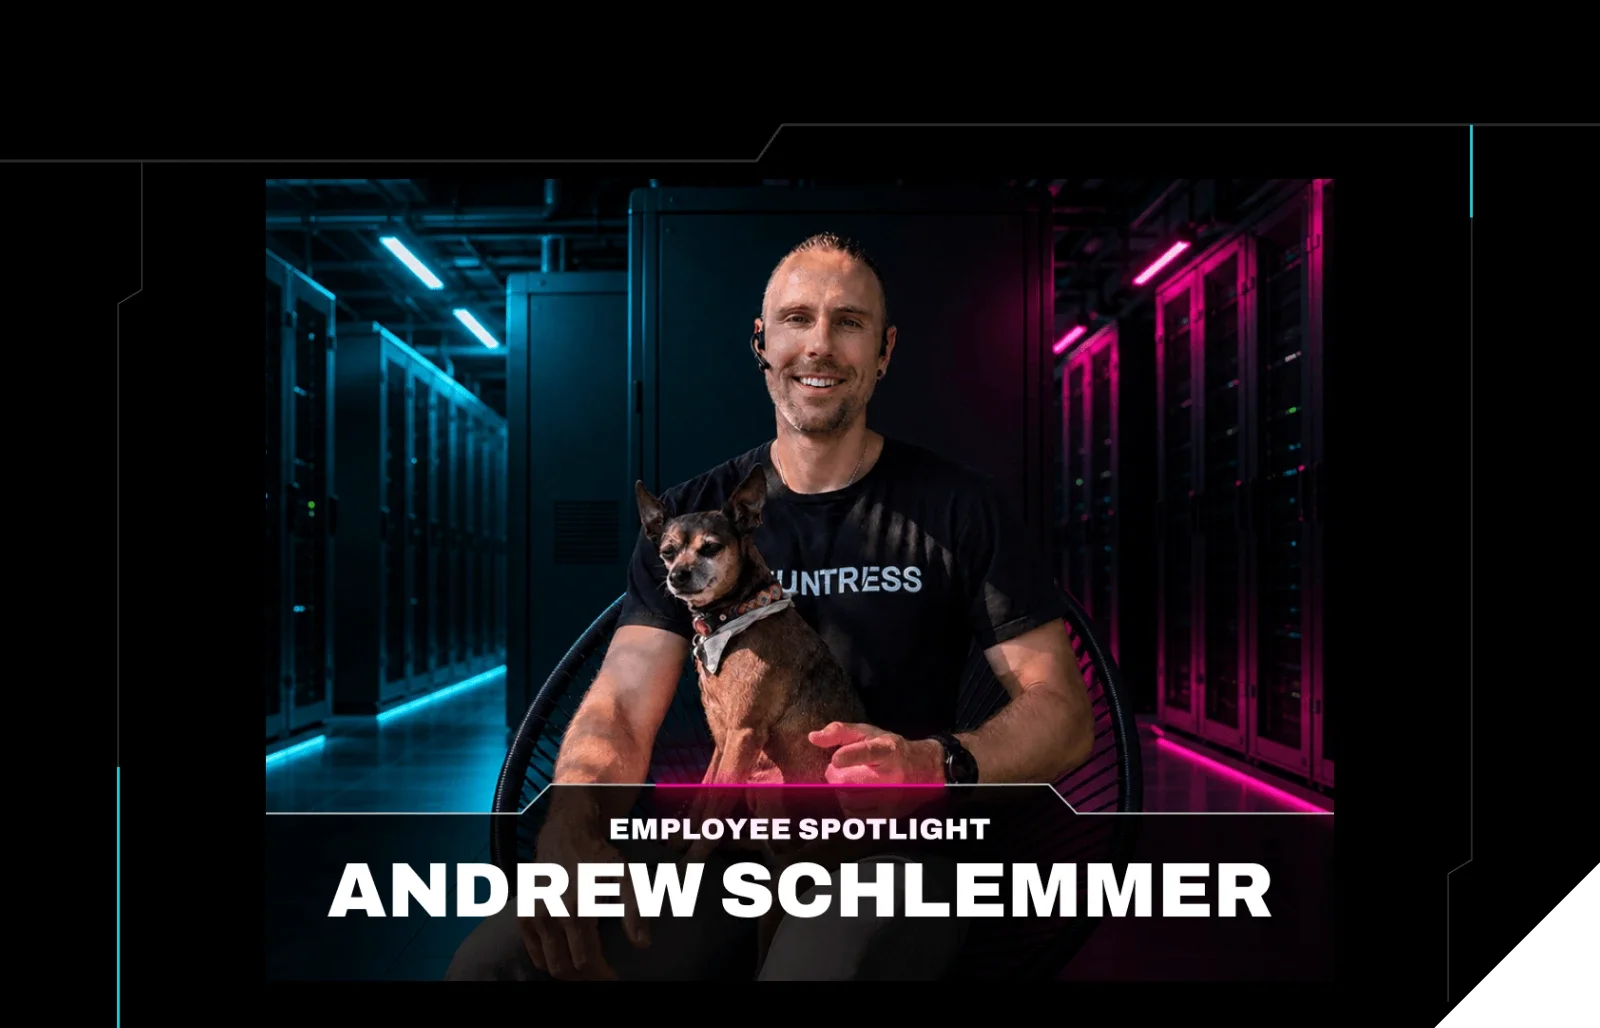
Employee Spotlight: Andrew Schlemmer
Andrew Schlemmer, a Channel Account Manager, was personally affected by cybercrime, an experience that shaped his professional mission. He now works to make enterprise-grade security solutions accessible and attainable for businesses of all sizes, using his firsthand understanding of cyber threats to drive his commitment to helping organizations better protect themselves.
DigiCert survey finds 81% of Australian organisations hit by AI security incidents or vulnerabilities
Matched: Australia
A DigiCert survey found that 81% of Australian organisations have experienced an AI-related security incident or identified AI-related vulnerabilities. The findings suggest AI security risks are already a widespread concern among Australian enterprises, highlighting the growing challenge businesses face in managing threats introduced or amplified by artificial intelligence adoption.