Cybersecurity News
Filters
Filtered by tag: law enforcement × Clear

Two Australians Charged Over TeamPCP Supply-Chain Attacks That Hit 1,000+ Organizations
Matched: Australia, cryptocurrency
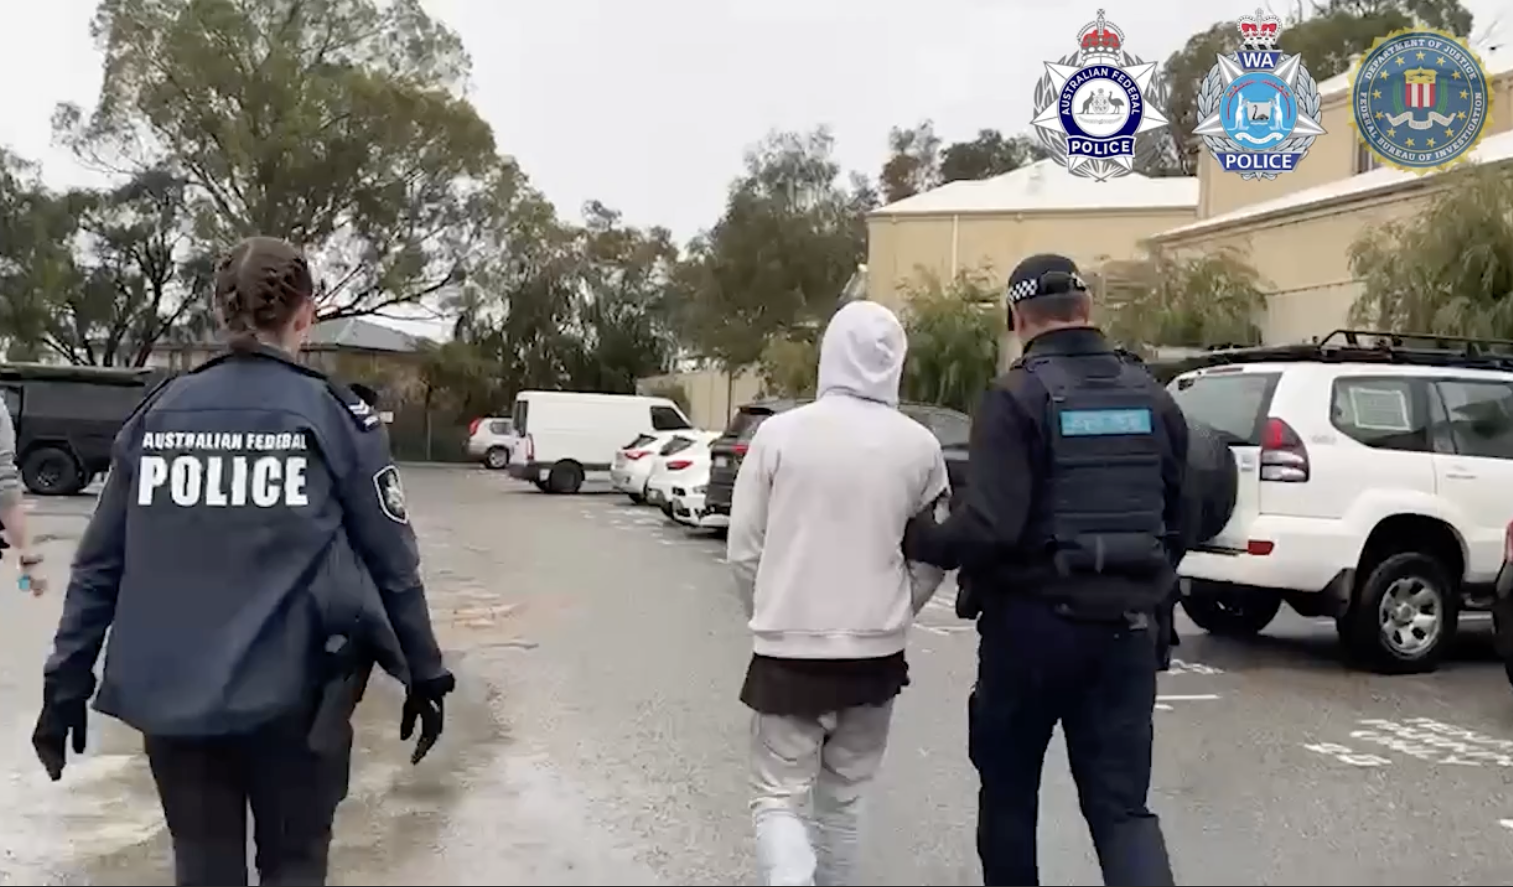
Two Western Australian men have been charged with 14 offenses over alleged supply-chain attacks attributed to TeamPCP. Investigators say the pair planted malicious code in open-source repositories, compromising over 1,000 organizations globally, stealing 500,000+ credentials and exfiltrating 300GB of data. Remediation costs are estimated in the hundreds of millions. Warrants were executed in Cottesloe, Hamilton Hill, and Mandurah on 26 August 2026, with FBI involvement. Both men appeared in Perth Magistrates Court on 27 August 2026.
Two Aussies alleged to be "principal participants" of TeamPCP hacking group
Matched: Australia
Australian and US authorities have taken coordinated action against two Australians allegedly identified as principal participants in the TeamPCP hacking group. No further details about the nature of the charges, the individuals named, or the specific actions taken by authorities were provided beyond their alleged central roles in the group.
Busted! Interpol-led operation targeting West African cybercrime groups nets 58 arrests
Matched: Australia
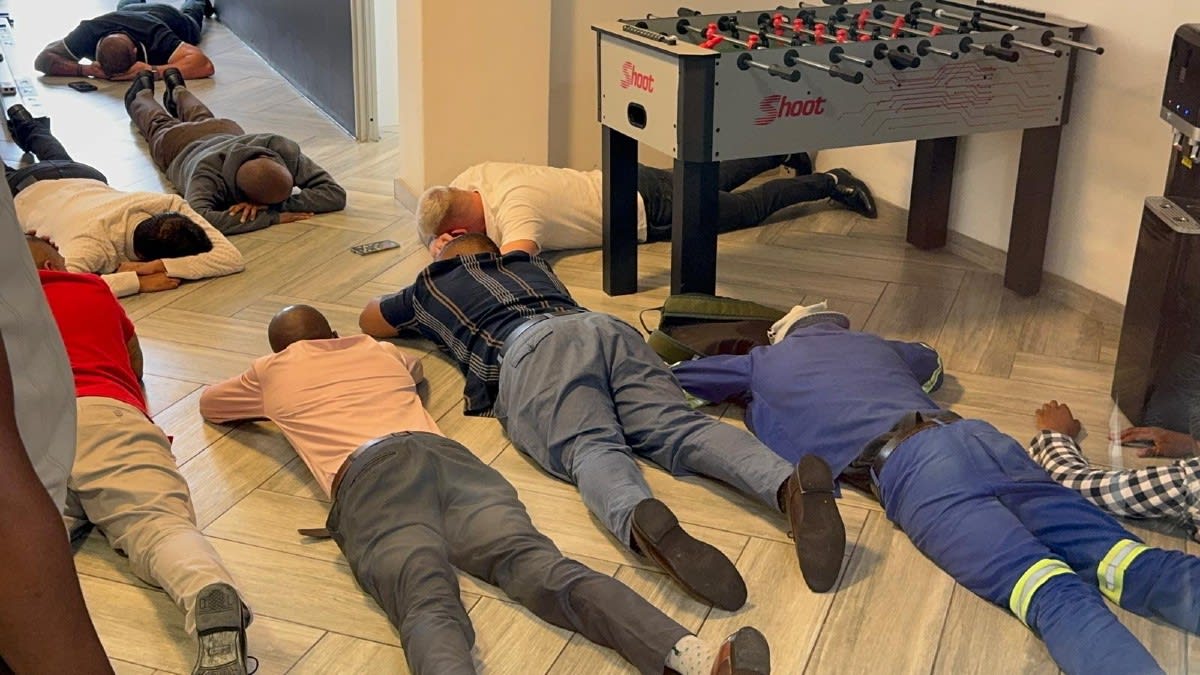
Interpol's Operation Jackal IV, involving 22 countries across six continents including Australia, resulted in 58 arrests targeting West African cybercrime groups. The operation focused on disrupting romance scams and cryptocurrency fraud networks. Authorities also blocked hundreds of suspicious bank accounts and seized assets as part of the coordinated crackdown on organized cybercriminal activity.
FBI Seizes NetNut Proxy Platform, Popa Botnet
The FBI seized hundreds of domains tied to NetNut, a residential proxy service run by Israeli company Alarum Technologies. The action followed a KrebsOnSecurity report linking NetNut to the Popa botnet, a network of at least two million devices infected without owner consent. The seizure involved industry partners and came roughly two weeks after the security findings were published.