Cybersecurity News
Filters
Filtered by tag: remote code execution × Clear

PaperCut NG/MF Vulnerability Actively Exploited in Attack – All Versions Impacted
Matched: Australia
PaperCut has confirmed active exploitation of an unpatched flaw affecting all supported versions of its PaperCut NG and MF print management software. Emergency patches for v25 and v26 were released on August 28, 2026; a v24 fix is pending. Organizations with internet-facing servers are urged to restrict access via firewall rules immediately and watch for suspicious activity from pc-app.exe or anomalous log entries.
From Screen Share to Root Access: Breaking Down CVE-2026-43760 and CVE-2026-65400 on macOS
Two vulnerabilities in macOS's Screen Sharing server were patched in a recent Apple update. CVE-2026-43760 allows pre-authenticated remote code execution, meaning attackers need no credentials to exploit it. CVE-2026-65400 can grant root-level access. Together, the flaws present a serious risk to users with Screen Sharing enabled. Apple has released fixes and users are urged to update immediately.
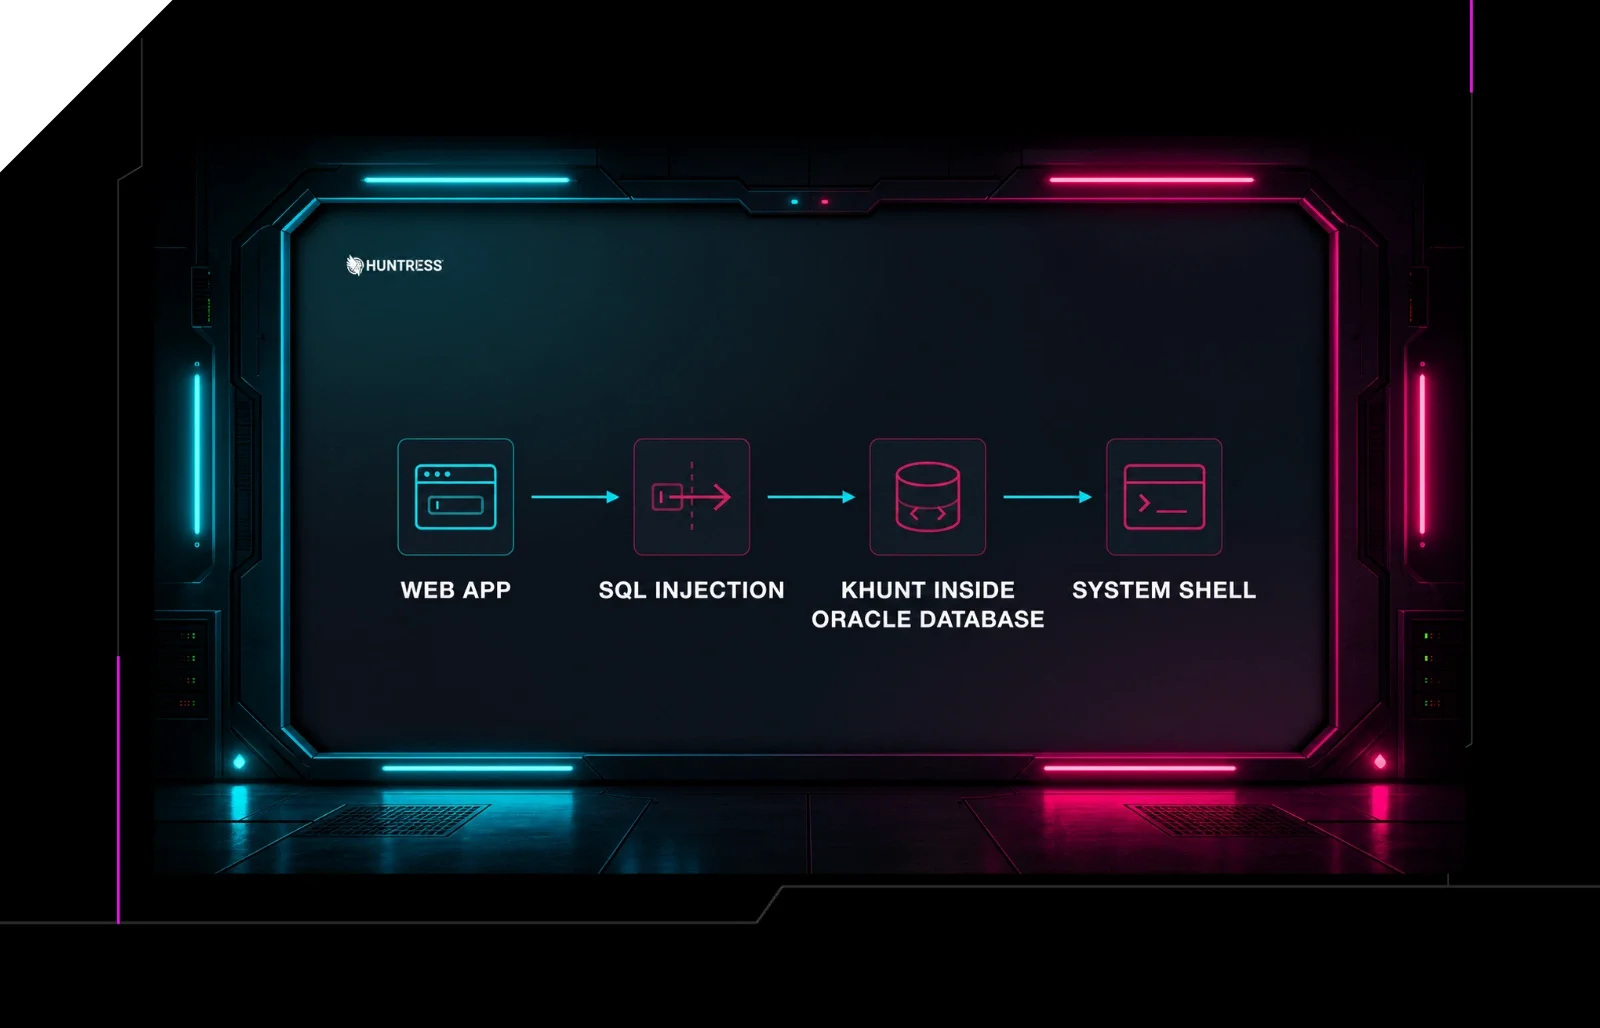
Inside an Oracle Database SQL Injection Attack | Huntress
Attackers exploited a SQL injection vulnerability in an Oracle Database-connected application to achieve full OS-level remote code execution. By abusing Oracle's built-in Java functionality, they compiled and executed malicious Java source code directly within the database, ultimately deploying the Khunt post-exploitation toolkit for further access and lateral movement.