Cybersecurity News
Filters
Filtered by tag: reverse engineering × Clear
Security expert hijacks Apple's Find My network to share data with a Linux device
A security researcher registered a Linux machine as a trusted Apple device, gaining access to Find My location-sharing data normally restricted to Apple hardware. The technique required reverse-engineering Apple's private protocols, obtaining identity certificates, and registering the machine as a legitimate node — accomplished in under a week without jailbreaking or leaked keys. Critically, it still requires a contact's prior consent to share location and cannot silently track strangers. Apple has not responded to inquiries.
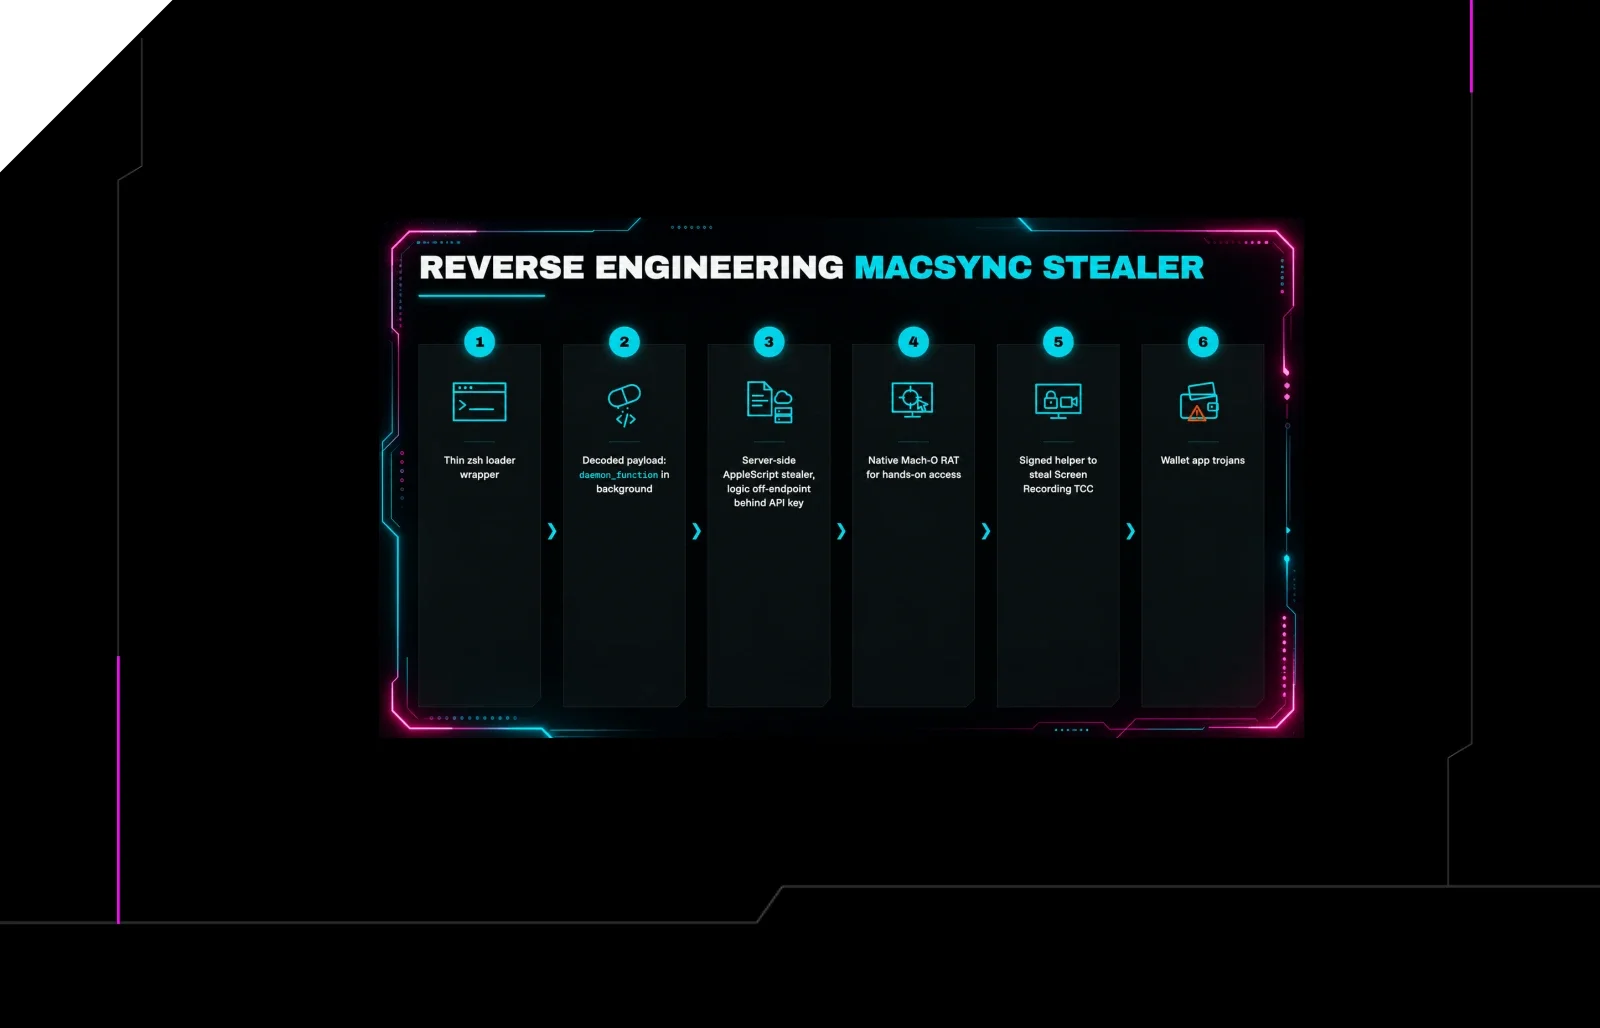
Reverse Engineering the Six Stages of MacSync Stealer and RAT
Researchers reverse-engineered MacSync, a six-stage macOS malware combining stealer and remote access trojan capabilities. The sample was recovered from attacker infrastructure after the compromised host went offline. Analysis traced its execution chain across all six stages, revealing how it exfiltrates data and maintains remote access on infected machines.