Cybersecurity News
Filters
Filtered by tag: supply chain attack × Clear

Two Australians Charged Over TeamPCP Supply-Chain Attacks That Hit 1,000+ Organizations
Matched: Australia, cryptocurrency
Two Western Australian men have been charged with 14 offenses over alleged supply-chain attacks attributed to TeamPCP. Investigators say the pair planted malicious code in open-source repositories, compromising over 1,000 organizations globally, stealing 500,000+ credentials and exfiltrating 300GB of data. Remediation costs are estimated in the hundreds of millions. Warrants were executed in Cottesloe, Hamilton Hill, and Mandurah on 26 August 2026, with FBI involvement. Both men appeared in Perth Magistrates Court on 27 August 2026.

Alleged TeamPCP Hackers Charged in Australia Over Major Supply Chain Attacks
Matched: Australia
Two Western Australian men have been charged with 14 offences over their alleged roles in TeamPCP, a cybercrime group accused of compromising open-source security tools Trivy, Checkmarx KICS, and AI gateway LiteLLM in March 2026. Louis Michael Gaebler, 23, and Ruben Ian Thomson, 21, appeared in Perth Magistrates Court on August 27.
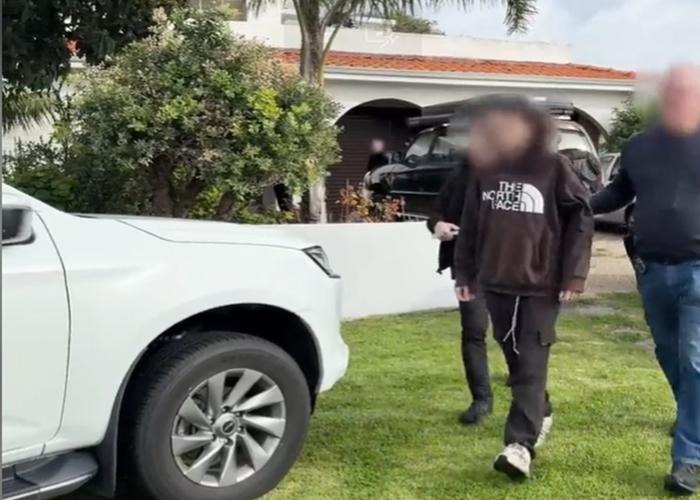
Two WA men charged after AFP-FBI-WAPF probe into alleged open-source supply-chain attack
Matched: Australia
Two Western Australian men have been charged with 14 offences following a joint investigation by the AFP, FBI, and WA Police into an alleged cybercrime syndicate. The group allegedly tampered with open-source software to gain unauthorised access to corporate networks, stealing data and extorting victims. The investigation highlights growing concerns about supply-chain vulnerabilities in widely used open-source tools.
North Korean Hackers Tied to Rust Supply Chain Attack
North Korean hackers have been linked to a supply chain attack targeting the Rust programming ecosystem. Researchers identified malicious backdoors embedded in compromised Rust packages, connecting the campaign to previously documented North Korean threat actors. The attack follows a pattern of supply chain intrusions attributed to the group, raising fresh concerns about open-source package repository security.
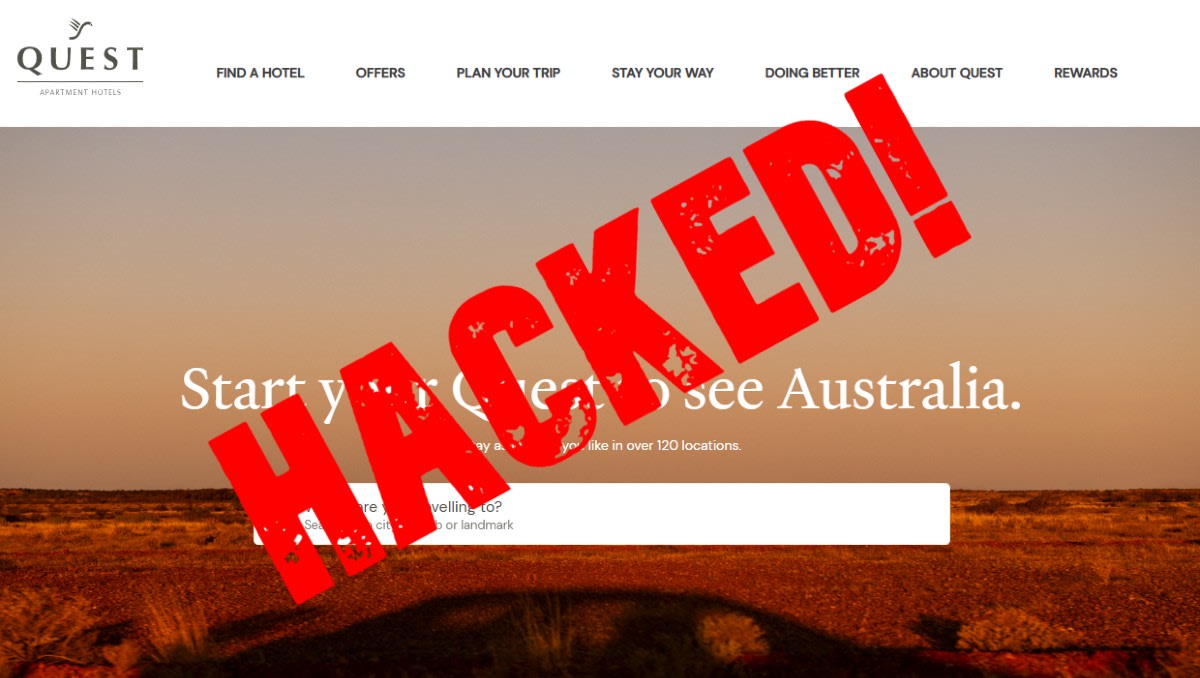
Faulty towers: Quest hotel chain discloses third-party customer data breach
Matched: Australia
Australian hotel apartment chain Quest has disclosed a data breach affecting customer information, including names, email addresses, and dates of birth. The breach originated from a third-party supplier rather than Quest's own systems. Affected customers have been notified and warned to remain vigilant against potential phishing attempts and scams that may exploit the compromised data.
Pokémon Center data breach exposes customer info, cancels some orders
Pokémon Center has disclosed a data breach affecting customer information, stemming from a cyberattack on logistics partner CEVA Logistics. As a result, some orders have been cancelled or delayed. The incident is part of a broader supply chain attack targeting CEVA Logistics, with Pokémon Center among several companies affected. Customers are advised to monitor their accounts for suspicious activity.

Malicious Solidity Pro VS Code Extension Steals Crypto Wallets, API Keys and SSH Keys via Telegram
Matched: cryptocurrency
A malicious VS Code extension called Solidity Pro has been discovered stealing cryptocurrency wallet data, API keys, and SSH keys from developers. Disguised as a legitimate Solidity development tool with polished documentation, the extension exfiltrates stolen data via Telegram. The attack highlights how convincing branding and familiar tooling can lower developers' guard against supply chain threats.

Hackers Turned a Trusted Advertising Platform Into a Crypto-Stealer Delivery Network
Matched: cryptocurrency
Adform, an ad tech firm serving ~14,000 businesses, suffered a supply chain attack where hackers hijacked a widely used JavaScript file within its infrastructure to distribute cryptocurrency-stealing malware. Researcher Kevin Beaumont uncovered the breach, which exploited the platform's trusted ad-serving network to reach victims. Adform holds nearly 30% of the demand-side platform market, amplifying the attack's potential reach.

Hackers Poison Adform Script to Swap Crypto Wallet Addresses Across Customer Sites
Matched: cryptocurrency
Attackers modified a JavaScript file from ad tech firm Adform to silently replace cryptocurrency wallet addresses in users' browsers. The malicious script, active on July 27, 2026, targeted Bitcoin and other crypto addresses copied by visitors to affected sites. Adform detected and removed the code the same day, notified clients, and reported the incident to authorities. Users who transacted on July 27 should verify their wallet addresses.