
Cybersecurity News
Filters
Filtered by tag: identity security × Clear
'It is significant, and it’s something many organisations haven't accounted for': The phishing threats hiding in your calendar invites
Hackers are increasingly using calendar invites and .ics files as phishing vehicles, exploiting the trust users place in scheduling tools. Unlike emails, calendar entries are added automatically, persist even after source emails are deleted, and often escape traditional security inspection. They can contain malicious links, QR codes, and fake branding. Experts recommend treating .ics files like attachments, using phishing-resistant MFA, and training staff to question unexpected calendar-based HR or payroll notifications.
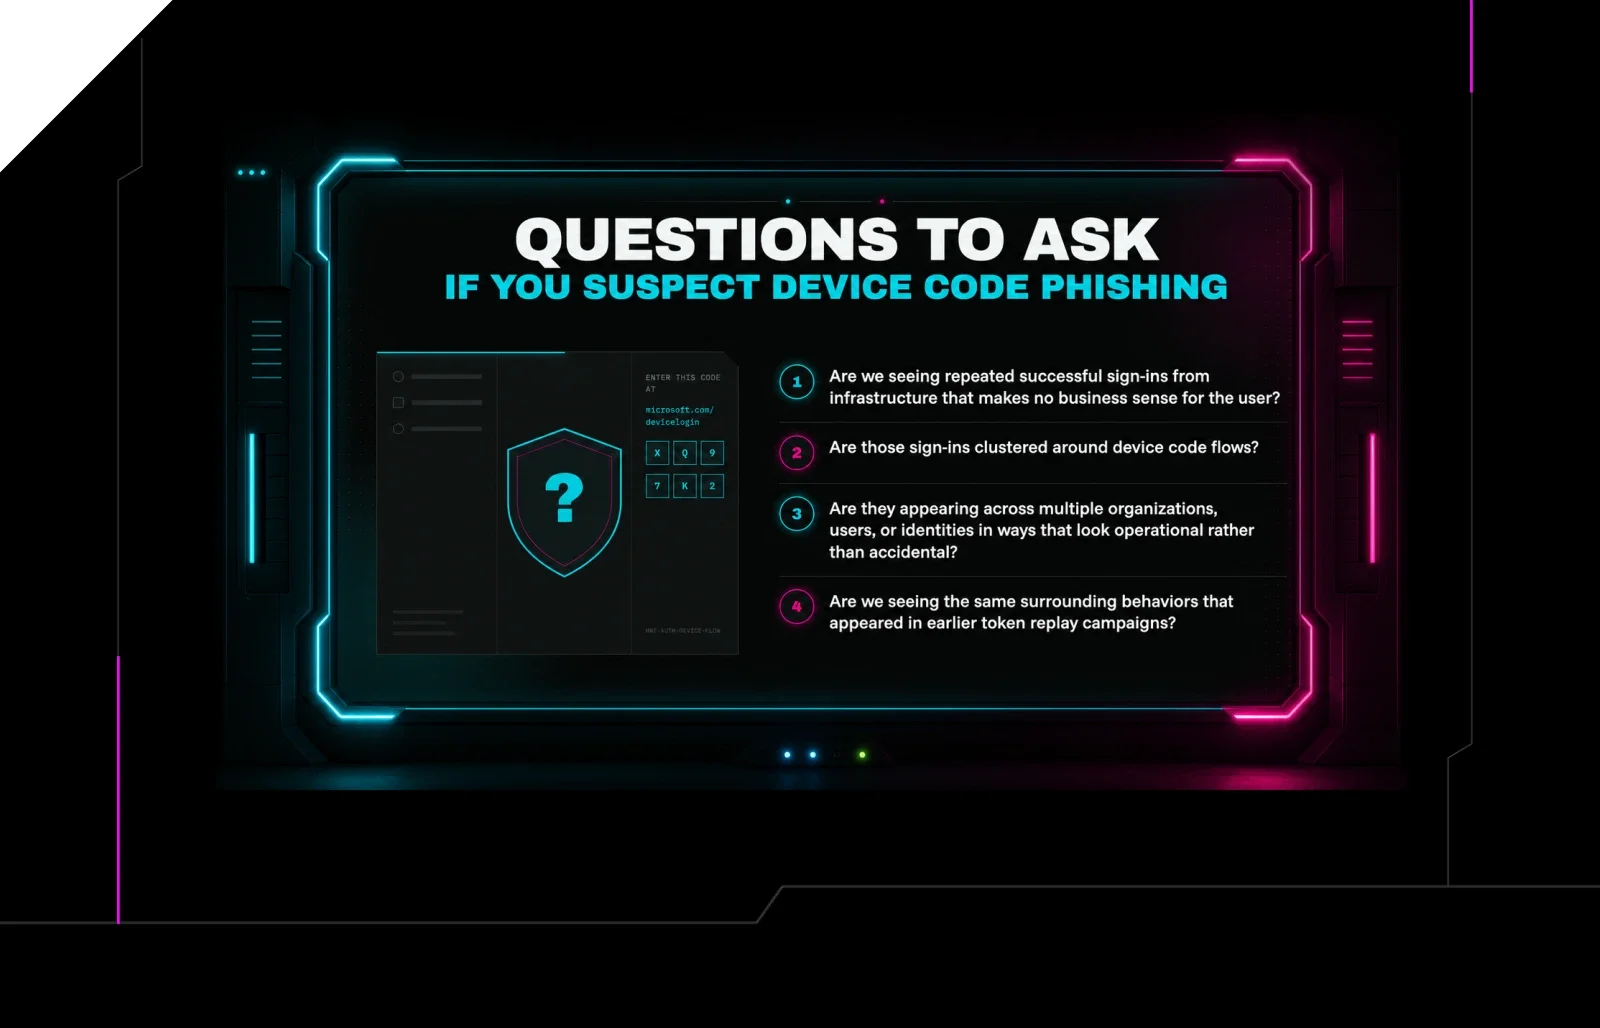
Device Code Phishing Keeps Evolving. Here’s What to Watch For
Attackers are abusing Microsoft 365's device code authentication flow to steal tokens without needing credentials. Victims are tricked into entering attacker-generated codes at legitimate Microsoft login pages, granting persistent access. The technique bypasses MFA and leaves minimal obvious indicators. Huntress advises monitoring for unusual device code authentication requests, unexpected token grants, and sign-ins from unfamiliar locations or clients.
How the LSHIY Password-Spraying Attack Abuses OAuth’s ROPC Grant
Researchers tracked a large automated password-spraying campaign targeting Azure CLI that exploited OAuth's Resource Owner Password Credentials grant, a deprecated flow still supported by many systems. Attackers used it to avoid modern authentication defenses like MFA prompts and conditional access policies. The campaign, dubbed LSHIY, highlights risks of legacy OAuth flows remaining enabled, and researchers recommend disabling ROPC grants where possible.
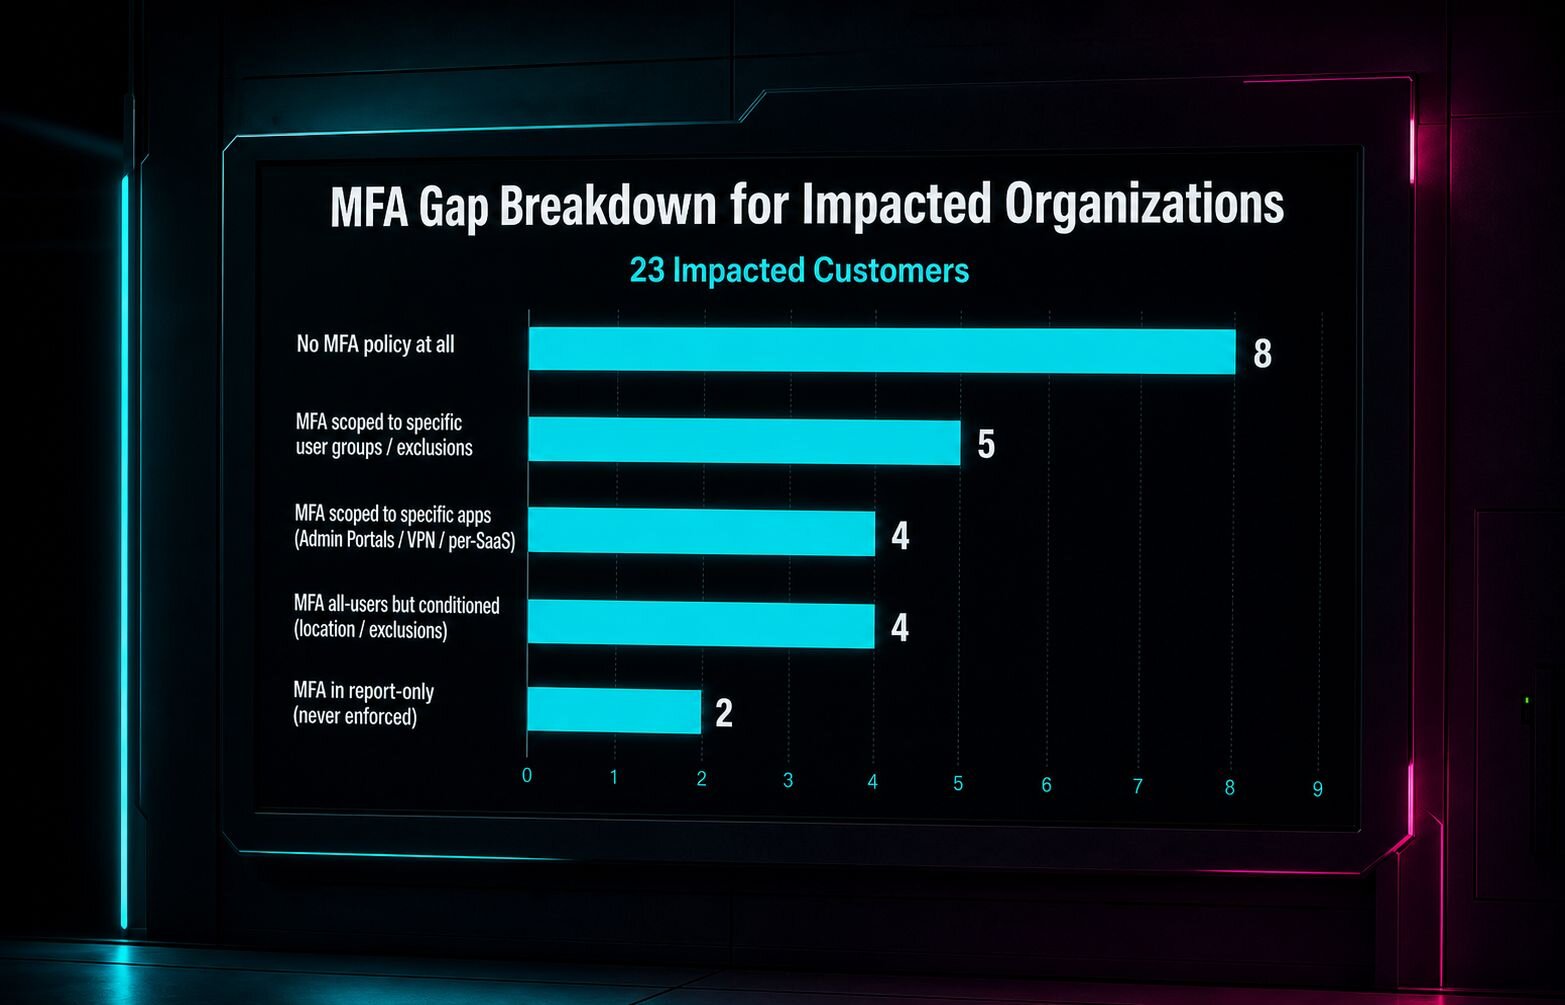
Conditional Access Misconfigurations Exposed 55 Orgs with MFA On
Huntress researchers found that Conditional Access misconfigurations left 55 organizations vulnerable despite having MFA enabled. Two real attack cases bypassed policies that appeared properly set up, exposing gaps invisible to standard reviews. Huntress's Managed Identity Security Posture Management tool is designed to detect these configuration flaws before attackers can exploit them.