
Cybersecurity News
Filters
Filtered by tag: stealer × Clear

ClickFix Campaigns Deploy PavinLoader With Blockchain-Based C2 and Amatera Stealer
Matched: cryptocurrency
ClickFix campaigns are delivering PavinLoader malware through fake CAPTCHA pages, software downloads, and malicious game installers that trick users into running malicious commands. The loader uses legitimate Windows tools like MSBuild to hide its activity, employs blockchain-based command-and-control via EtherHiding to obscure infrastructure, and deploys payloads including Amatera Stealer and HijackLoader to steal passwords, browser data, and cryptocurrency wallet information.

ClickFix Attacks Deliver macOS Stealer That Can Drain Crypto Wallets
Matched: cryptocurrency
A ClickFix-style attack campaign is targeting macOS users with Go-based malware that steals cryptocurrency, browser passwords, Apple iCloud Keychain data, and cached credentials. The infection chain uses a shell script to profile the host before delivering a CPU-compatible payload, allowing attackers to drain crypto wallets and harvest sensitive data from compromised machines.
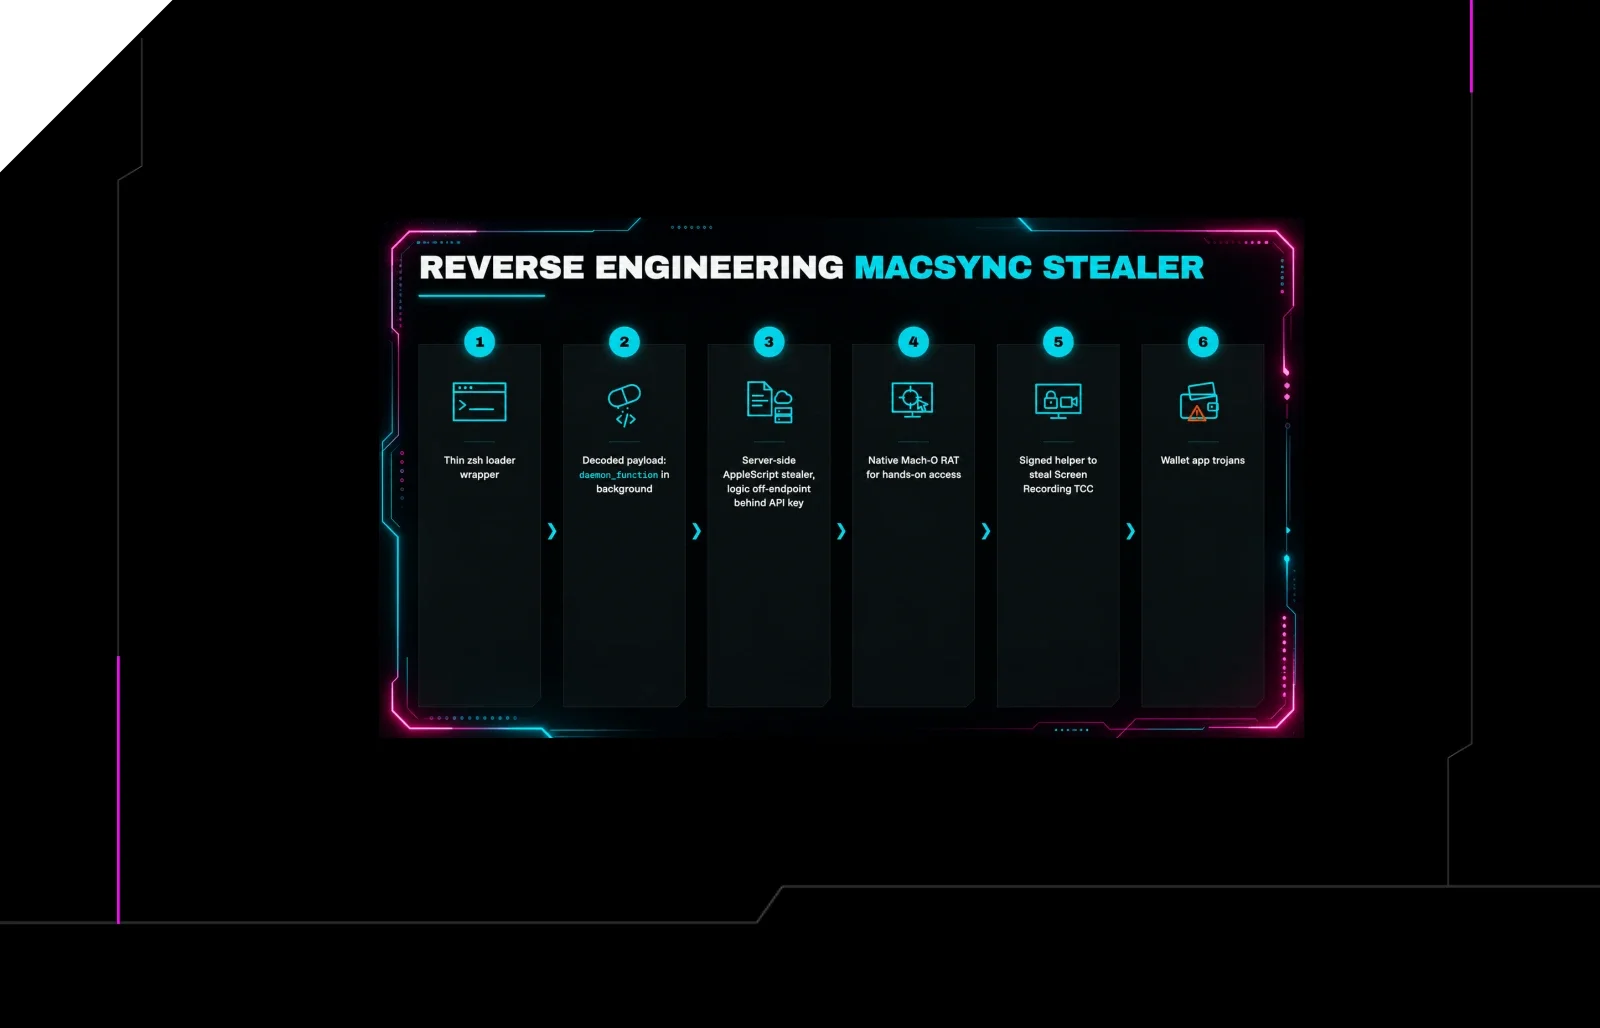
Reverse Engineering the Six Stages of MacSync Stealer and RAT
Researchers reverse-engineered MacSync, a six-stage macOS malware combining stealer and remote access trojan capabilities. The sample was recovered from attacker infrastructure after the compromised host went offline. Analysis traced its execution chain across all six stages, revealing how it exfiltrates data and maintains remote access on infected machines.