
Cybersecurity News
Filters
Filtered by tag: remote code execution × Clear

Fortinet Urges Customers to Patch Critical Flaws Affecting FortiOS, FortiManager, and FortiAnalyzer
Matched: OpenAI
Fortinet is urging customers to apply security updates releasing October 22 for FortiOS, FortiManager, FortiAnalyzer, FortiMail, and FortiAuthenticator, addressing critical and high-severity vulnerabilities. The company warns against treating patches as routine, noting attackers can use AI-assisted patch diffing to build exploits within hours. Public advisories will follow on November 10, but Fortinet asks customers to act immediately, prioritizing internet-facing devices.

October 21 Cybersecurity Nightmare: PHP and Node.js Flaws, LiteLLM Backdoor, and Active Attacks
Matched: cryptocurrency
Multiple critical security issues emerged October 21, 2026. PHP patches addressed two RCE flaws (CVSS 9.2); Node.js fixed ten vulnerabilities including a Brotli decompression RCE. LiteLLM version 1.107.0 contained credential-stealing malware; AWS keys were misused within hours. WordPress plugin firm UpdraftPlus suffered a management key breach. OVHcloud CLI binaries were briefly replaced. Eight eMudhra certificate authority signing keys were found recoverable from public certificates. Palo Alto GlobalProtect and Plex servers faced active exploitation. Patching alone is insufficient where credentials or backdoors may already exist.
Australian Cybersecurity Magazine
Critical PHP vulnerabilities allow remote execution
Matched: Australia
Australia's cyber security agency has warned of two critical PHP vulnerabilities flagged by the PHP Foundation. The flaws could allow remote code execution, posing significant risk to systems running affected PHP versions. Users and administrators are urged to apply patches promptly and follow guidance from both the ACSC and PHP Foundation to mitigate potential exploitation.

Widespread PHP Flaw May Cause Many Site Outages Today
Matched: OpenAI
A critical pair of PHP vulnerabilities affecting roughly 70% of websites is being actively exploited, with working exploits already circulating. All PHP versions since 5.4 are affected, enabling remote code execution, denial-of-service, and data exposure. Fixes are available in PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35. Cloudflare implemented firewall protections early today, while government sites in Europe have already gone offline. Researchers compare the severity to the 2021 Log4Shell flaw.

PHP Releases Emergency Patches for PHP2Shell Flaws Threatening Millions of Web Servers
Matched: OpenAI
PHP has released emergency patches for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, dubbed PHP2Shell, which could allow unauthenticated remote code execution on web servers. Both carry a CVSS 4.0 score of 9.2. Fixed versions are PHP 8.2.35, 8.3.36, 8.4.27, and 8.5.12. Administrators should update immediately and restart PHP workers to ensure patched versions are active across all services.

Langflow's Critical Authenticated RCE Flaw Targeted in 1,423 Honeypot Exploit Attempts
Matched: Artificial Intelligence
A critical flaw in Langflow (CVE-2026-105740, CVSS 9.9) is being actively exploited, with 1,423 attempts recorded on honeypots. The vulnerability affects the open-source AI workflow platform, now owned by IBM following its February 2025 acquisition of DataStax. The flaw allows authenticated remote code execution, prompting security alerts from Previdian urging users to patch immediately.

PaperCut NG/MF Vulnerability Actively Exploited in Attack – All Versions Impacted
Matched: Australia
PaperCut has confirmed active exploitation of an unpatched flaw affecting all supported versions of its PaperCut NG and MF print management software. Emergency patches for v25 and v26 were released on August 28, 2026; a v24 fix is pending. Organizations with internet-facing servers are urged to restrict access via firewall rules immediately and watch for suspicious activity from pc-app.exe or anomalous log entries.
From Screen Share to Root Access: Breaking Down CVE-2026-43760 and CVE-2026-65400 on macOS
Two vulnerabilities in macOS's Screen Sharing server were patched in a recent Apple update. CVE-2026-43760 allows pre-authenticated remote code execution, meaning attackers need no credentials to exploit it. CVE-2026-65400 can grant root-level access. Together, the flaws present a serious risk to users with Screen Sharing enabled. Apple has released fixes and users are urged to update immediately.
Inside an Oracle Database SQL Injection Attack | Huntress
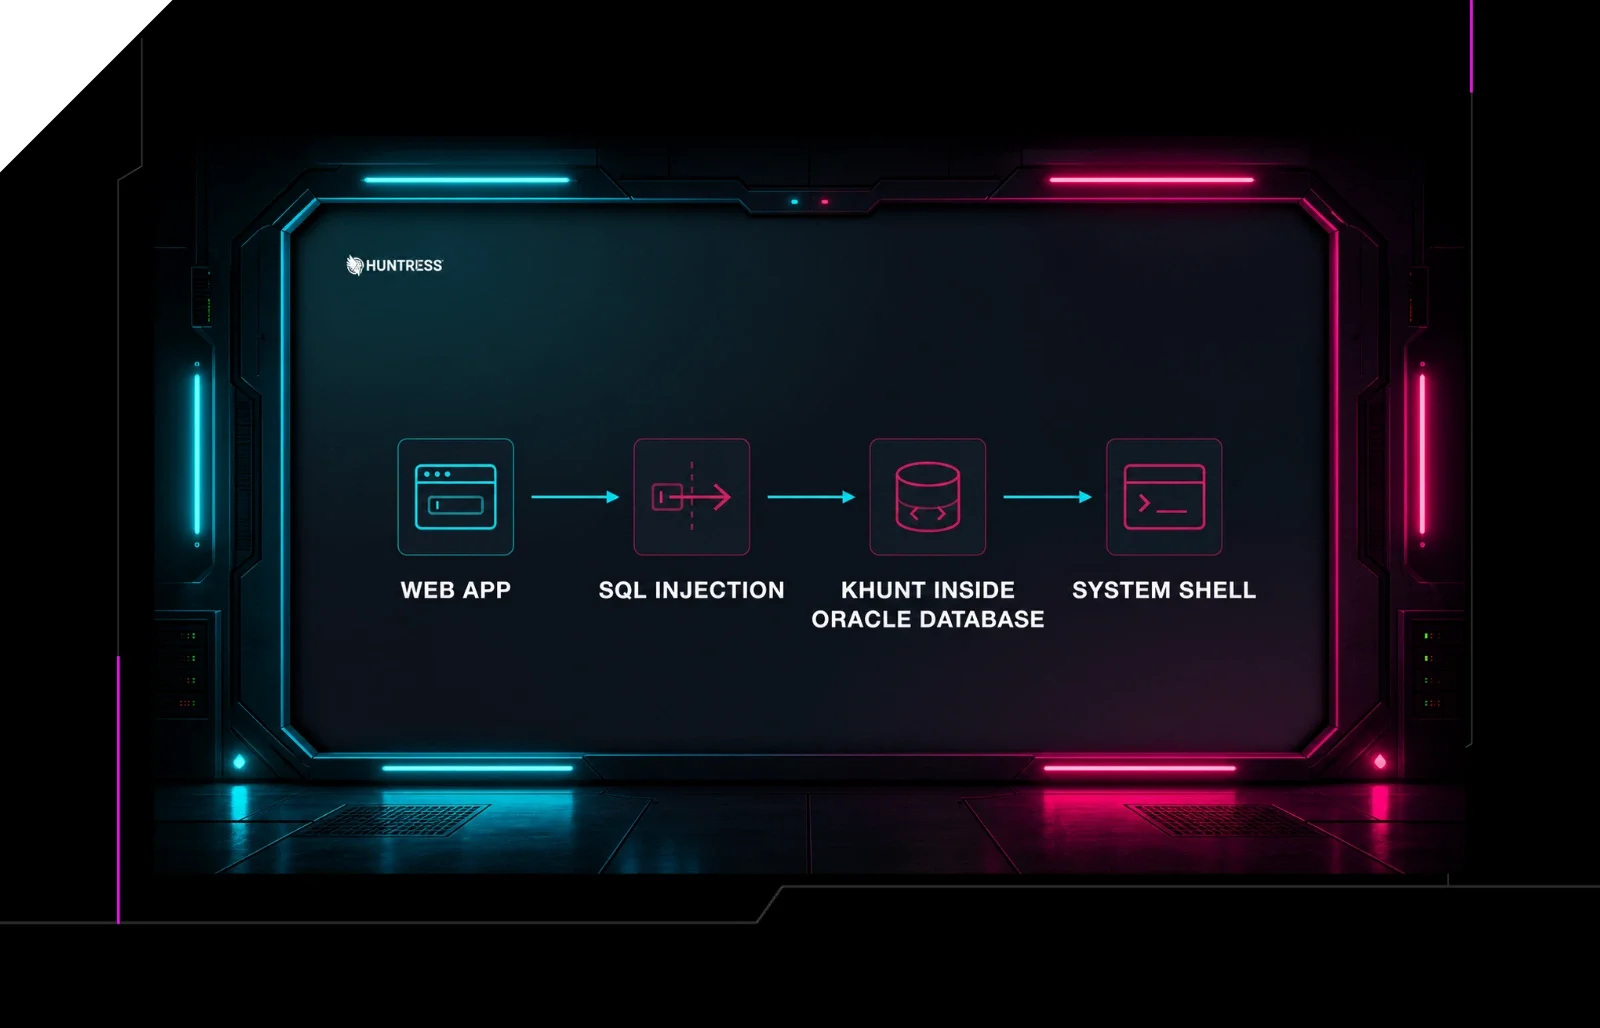
Attackers exploited a SQL injection vulnerability in an Oracle Database-connected application to achieve full OS-level remote code execution. By abusing Oracle's built-in Java functionality, they compiled and executed malicious Java source code directly within the database, ultimately deploying the Khunt post-exploitation toolkit for further access and lateral movement.