Cybersecurity News
Filters
Filtered by tag: apple × Clear
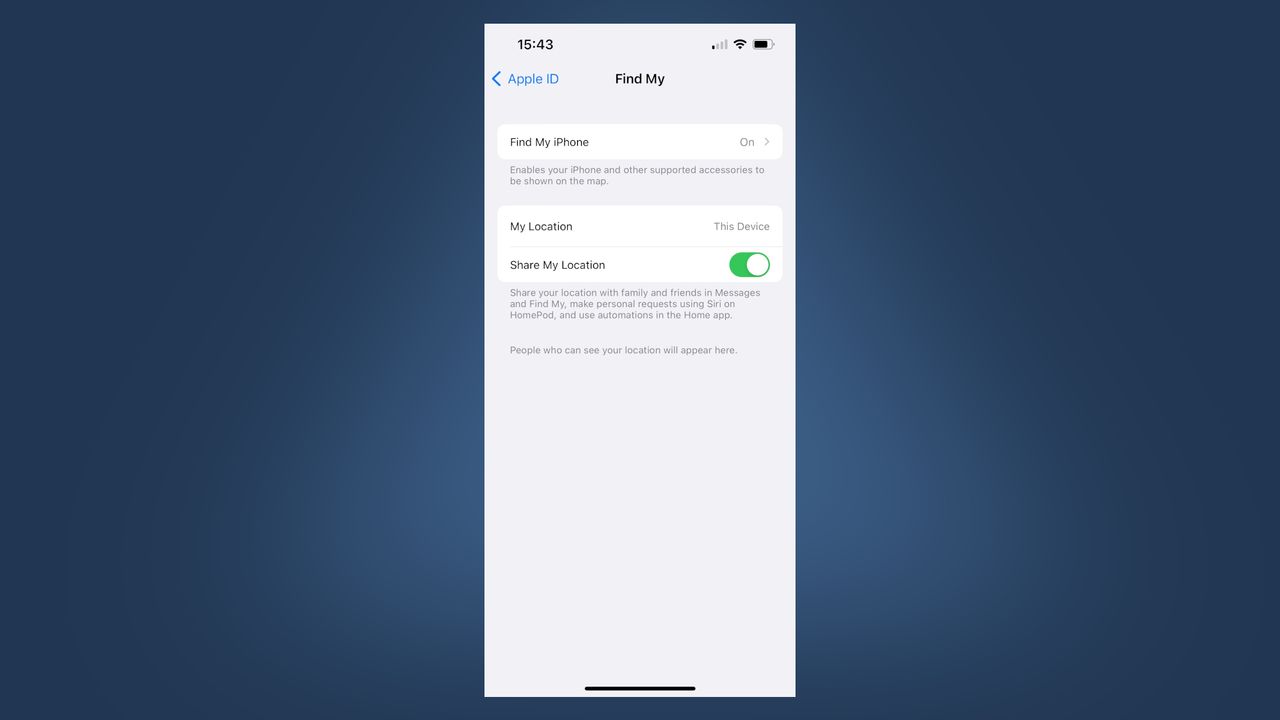
Security expert hijacks Apple's Find My network to share data with a Linux device
A security researcher registered a Linux machine as a trusted Apple device, gaining access to Find My location-sharing data normally restricted to Apple hardware. The technique required reverse-engineering Apple's private protocols, obtaining identity certificates, and registering the machine as a legitimate node — accomplished in under a week without jailbreaking or leaked keys. Critically, it still requires a contact's prior consent to share location and cannot silently track strangers. Apple has not responded to inquiries.
New 'AnonyMous' phishing campaign targets iPhone users with fake AI Apple support calls
AnonyMousKIT is a phishing kit targeting iPhone theft victims by exploiting Apple's Lost Mode contact feature. Attackers use victims' displayed contact info to impersonate Apple support via email, SMS, or AI-powered calls, directing them to fake Find My pages to steal credentials. Active since 2024, the operation runs 500+ domains, 150+ reseller brands, and AI voice agents costing $0.10 per call, primarily targeting Brazil, South Africa, India, Indonesia, Kenya, and Italy.
MacOS users warned to beware screen-sharing bug which can turn Macs into cryptomining slaves
Apple has patched a critical vulnerability in macOS Screen Sharing that could allow attackers to gain unauthorized access to devices and use them for cryptomining. The flaw posed significant risk to affected users. MacOS users are urged to update their systems immediately to protect against potential exploitation.