
Cybersecurity News
Filters
Filtered by tag: china × Clear

China-Linked Hackers Use ARTEX AI to Target 2,250 Microsoft 365 Tenants After ConnectWise Breach
Matched: Claude
China-linked hackers using Storm-0940 exploited the ConnectWise Cloud Backup breach to target over 2,250 Microsoft 365 tenants, using the AI-powered penetration framework ARTEX. Attackers abused stolen application credentials rather than passwords, authenticating as trusted apps and using Microsoft Graph to alter permissions. Microsoft and Zscaler published findings October 21, noting some attacks achieved privileged access in under three hours.

China-Linked Hackers Use ARTEX AI Agents in ConnectWise Supply Chain Attack
Matched: Agentic
Microsoft linked Chinese state actor Storm-0940 to a supply chain attack on ConnectWise's Cloud Backup application. The group used ARTEX, a closed-source Go-based AI penetration testing framework, to accelerate scanning during the intrusion. ARTEX was made private after earlier abuse targeting South Korean financial institutions.
Trump signs order banning some foreign equipment from US energy grid, including some software
Matched: health
Trump has reissued a 2020 executive order declaring a national emergency over foreign bulk-power systems in the US energy grid, banning their purchase, import, or installation if deemed a national security risk. The order, widely seen as targeting Chinese equipment, also requires a review of existing foreign-built hardware and software. The Energy Department has 120 days to develop enforcement rules.

FBI Shuts Down China-Linked Hacking Platforms Used to Target NASA and U.S. Networks
Matched: health
The DOJ and FBI seized domains tied to two China-linked hacking platforms, QScan and QTRouter, connected to PRC state-sponsored group QTFY, operating through Nanjing Xinjiuwei Network Technology. The platforms infected IoT devices and routed malicious traffic through proxy networks to conceal attack origins. Victims included NASA, the Federal Reserve, DOJ, and the U.S. Senate. Seized domains rendered both platforms inoperable.

China-Linked Jewelbug Uses XG-Web for Government Espionage and Crypto Fraud
Matched: cryptocurrency
China-linked threat actor Jewelbug conducts cyber espionage against governments and militaries while also running cryptocurrency fraud operations. Both activities are managed through a single control panel called XG-Web, a browser-based framework that converts victims' browsers into remote-control tools for data theft and access.
World-first autonomous ‘end-to-end’ AI attack against Taiwan tied to Chinese hackers — and the scariest part is that it was fully open source
Chinese hackers carried out what researchers describe as the first fully autonomous, end-to-end AI-driven cyberattack, targeting Taiwan. The attack was linked to China through recovered written documentation. Notably, it was conducted entirely using open-source AI tools, raising concerns that sophisticated AI-powered cyberattacks are now accessible without proprietary or classified technology.
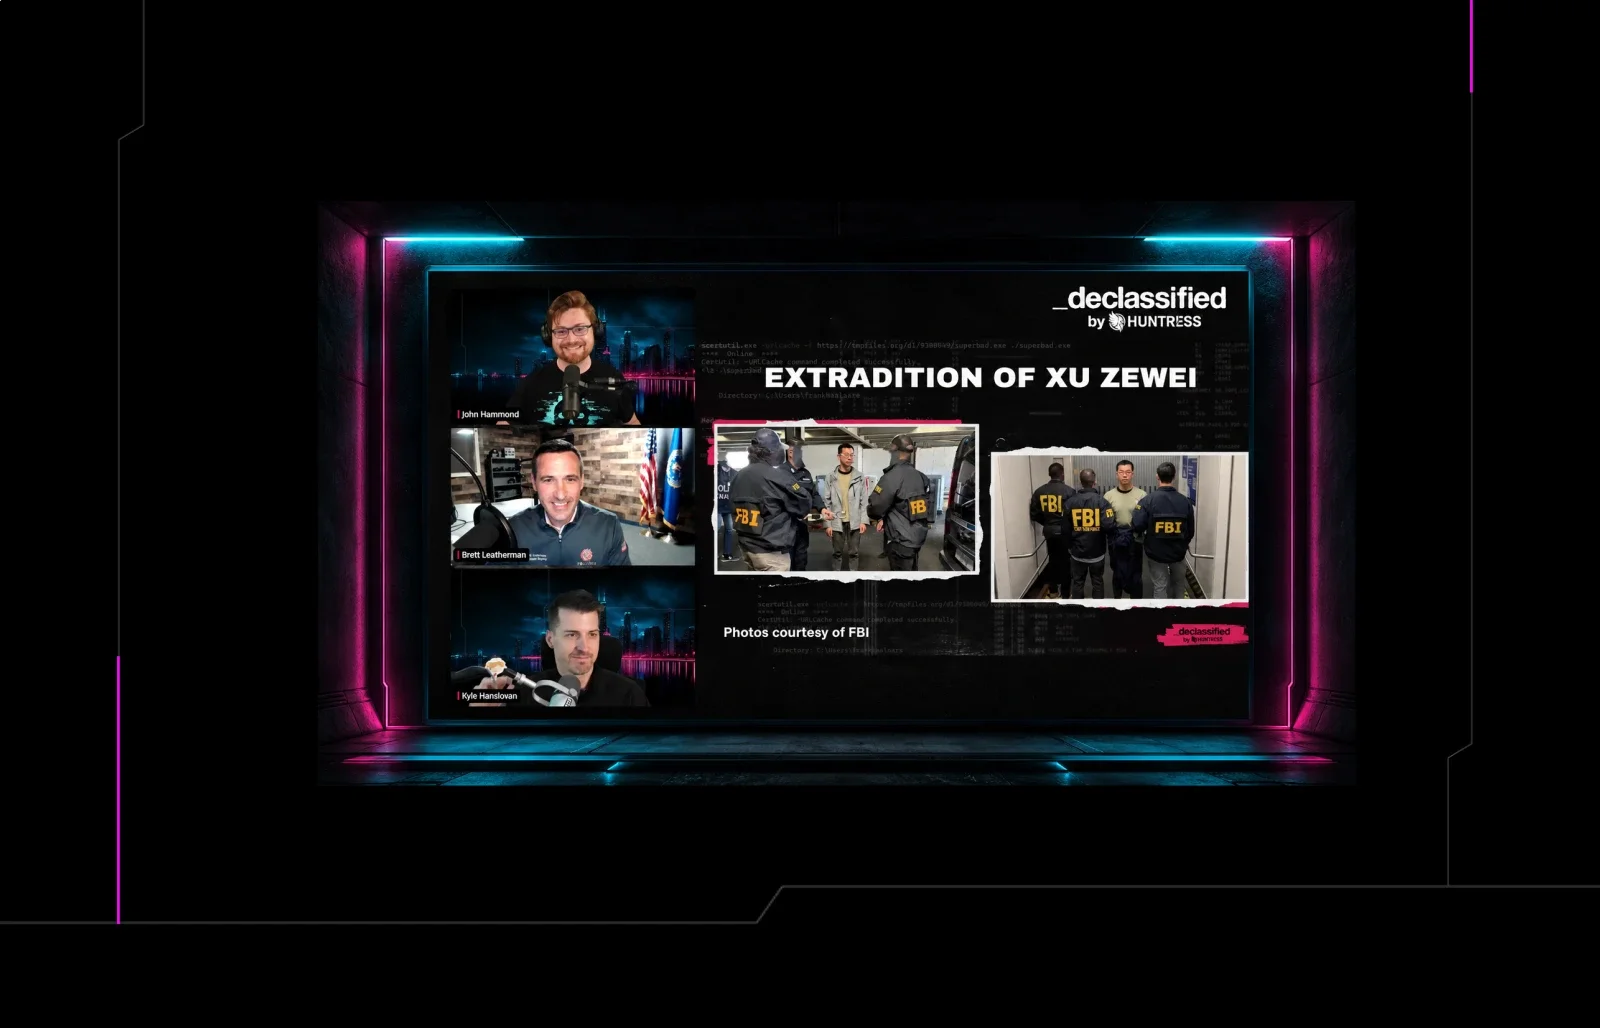
Five Years, 88,000 Backdoors, and a Pair of Handcuffs: Inside the Global Manhunt That Ended in an Arrest
A five-year joint investigation by cybersecurity firm Huntress and the FBI culminated in an arrest connected to Silk Typhoon, a Chinese state-linked hacking group. The operation tracked the deployment of roughly 88,000 backdoors in Microsoft Exchange servers. The case highlights the growing collaboration between private security researchers and federal law enforcement in combating sophisticated, state-sponsored cybercrime.