
Cybersecurity News
Filters
Filtered by tag: fbi × Clear

FBI Suspects Cybersecurity Executive Helped ShinyHunters Run Extortion Website
Matched: cryptocurrency, medical
The FBI suspects a US cybersecurity consulting executive helped hacking group ShinyHunters operate Shinywire, a website pressuring breached companies to pay ransoms. The site listed nearly 100 victim organizations and threatened data publication within seven days of non-response. Separately, Canadian executive Edward Dubrovsky, 54, was arrested October 8 in Pennsylvania on related extortion allegations. Investigators reportedly gained leads after Dutch police arrested a ShinyHunters suspect and accessed his Signal messages, which revealed contact with both executives. No charges have been filed against the unnamed firm executive. ShinyHunters is attributed with over $70 million in 2026 ransom payments.

FBI Arrests Executive at Ransomware Negotiation Firm
Matched: medical
FBI agents arrested Edward Dubrovsky, a Canadian cybersecurity executive specializing in ransomware negotiations, in Pennsylvania on cyber extortion and conspiracy charges. Dubrovsky, associated with firms Cypfer and CyberSteward, was attending a cyber insurance conference when arrested. His case has been moved to Texas, the center of the FBI's investigation into ShinyHunters, a hacking group that has extorted over $70 million this year and recently stole sensitive FBI personnel data.

FBI Probes Service Selling 153M+ Drivers Licenses
Matched: medical
A dark web service called Nexus was selling scans of over 153 million drivers licenses from the US and Canada, apparently stolen from Louisiana-based identity verification company IDScan.net. Timestamps on stolen records matched when victims used services at Hertz rental car locations and marijuana dispensaries. The FBI's New Orleans field office opened an investigation, and Nexus subsequently went offline. IDScan.net confirmed unauthorized access to customer data including names and ID numbers.

FBI Shuts Down China-Linked Hacking Platforms Used to Target NASA and U.S. Networks
Matched: health
The DOJ and FBI seized domains tied to two China-linked hacking platforms, QScan and QTRouter, connected to PRC state-sponsored group QTFY, operating through Nanjing Xinjiuwei Network Technology. The platforms infected IoT devices and routed malicious traffic through proxy networks to conceal attack origins. Victims included NASA, the Federal Reserve, DOJ, and the U.S. Senate. Seized domains rendered both platforms inoperable.
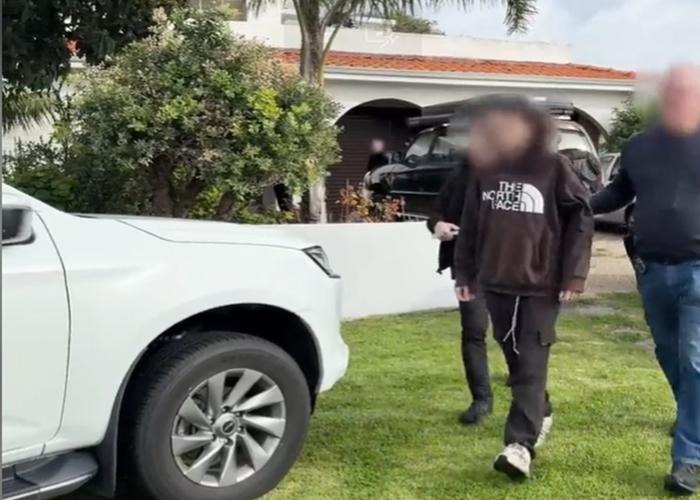
Two WA men charged after AFP-FBI-WAPF probe into alleged open-source supply-chain attack
Matched: Australia
Two Western Australian men have been charged with 14 offences following a joint investigation by the AFP, FBI, and WA Police into an alleged cybercrime syndicate. The group allegedly tampered with open-source software to gain unauthorised access to corporate networks, stealing data and extorting victims. The investigation highlights growing concerns about supply-chain vulnerabilities in widely used open-source tools.

CISA Warns Medusa Ransomware Hackers Steal Data, Kill Security Tools, and Encrypt Entire Networks
Matched: health
CISA, the FBI, and HHS have jointly issued an updated advisory warning that Medusa ransomware attackers are actively targeting enterprise networks, disabling security tools, stealing sensitive data, and encrypting entire systems. The alert urges organizations to strengthen defenses against the group, which has escalated its activity across critical sectors.
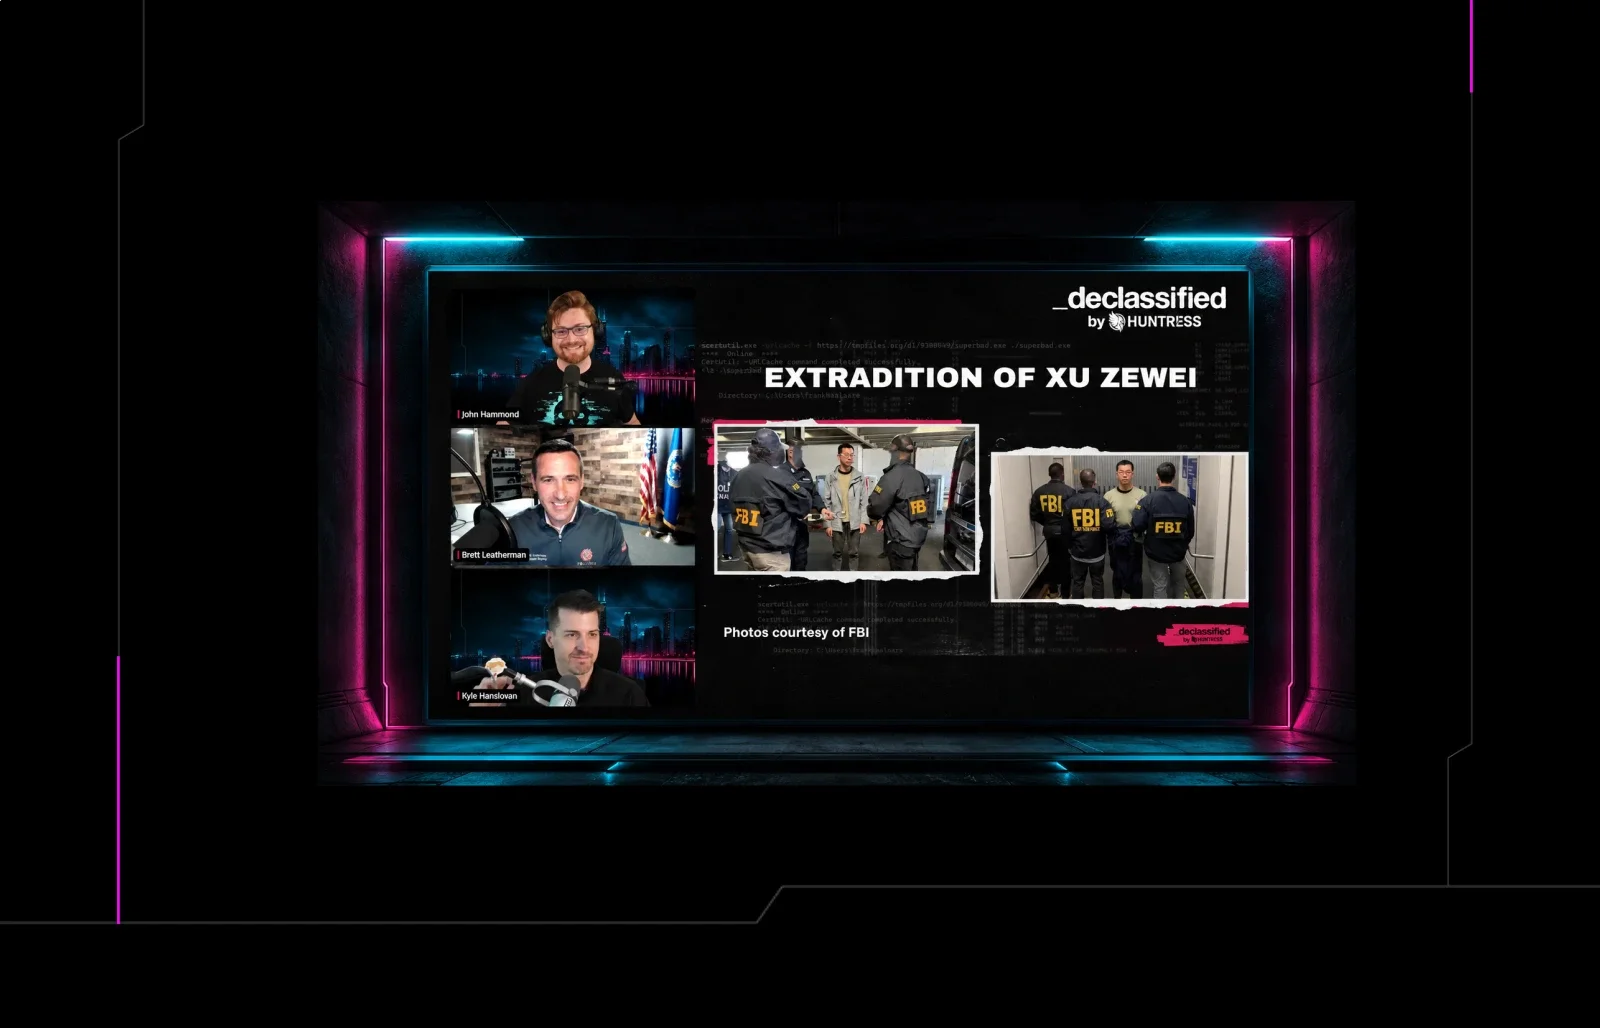
Five Years, 88,000 Backdoors, and a Pair of Handcuffs: Inside the Global Manhunt That Ended in an Arrest
A five-year joint investigation by cybersecurity firm Huntress and the FBI culminated in an arrest connected to Silk Typhoon, a Chinese state-linked hacking group. The operation tracked the deployment of roughly 88,000 backdoors in Microsoft Exchange servers. The case highlights the growing collaboration between private security researchers and federal law enforcement in combating sophisticated, state-sponsored cybercrime.