Cybersecurity News
Filters

Fake Microsoft Security Scan Tells You to Remove Antivirus—Then Scammers Ask for Remote Access
Matched: cryptocurrency, health
Scammers are running fake Microsoft-branded security scan websites that display fabricated results showing poor scores and false warnings. The sites instruct visitors to uninstall their antivirus software, then collect personal and banking details through a form before redirecting victims to await a callback. Callers then request remote access to the device. Malwarebytes identified 11 related sites sharing one server, all using similar SysScan branding.

ClickFix Campaigns Deploy PavinLoader With Blockchain-Based C2 and Amatera Stealer
Matched: cryptocurrency
ClickFix campaigns are delivering PavinLoader malware through fake CAPTCHA pages, software downloads, and malicious game installers that trick users into running malicious commands. The loader uses legitimate Windows tools like MSBuild to hide its activity, employs blockchain-based command-and-control via EtherHiding to obscure infrastructure, and deploys payloads including Amatera Stealer and HijackLoader to steal passwords, browser data, and cryptocurrency wallet information.

Microsoft August 2026 Update Breaks When Generating PDF/XPS Content
Matched: health
Microsoft's August 2026 .NET Framework cumulative updates are causing printing failures and PDF/XPS generation errors in WPF applications. The bug triggers a System.IO.FileFormatException when using ClearType fonts like Calibri, Cambria, Constantia, and Corbel, affecting Windows 10, 11, and Server 2012–2025. The issue stems from stricter font validation in the TrueType subsetter introduced alongside fixes for six security vulnerabilities. A temporary workaround exists but disables the security protections the update introduced.
Android car systems abused by hackers to launch new malware that pulls devices into a hidden proxy network
Kaspersky discovered Android malware targeting DoFun car head units by hijacking the TWCore update app to install malicious APKs. The multi-stage attack deploys a dropper, loader, and reverse proxy tool, with the apparent goal of building a botnet from internet-connected vehicles. Kaspersky attributed the campaign to MoYu Group, previously linked to the BadBox botnet. DoFun has since patched the vulnerabilities.
Some Mac users think they're installing OpenAI Codex, but it's actually a malware that can steal passwords in seconds
Matched: cryptocurrency
Cybercriminals are using stolen Google Ads accounts and Google Sites to impersonate OpenAI's Codex download page, targeting macOS users. The fake site avoids detection by hosting malicious content via an iFrame elsewhere. Victims are tricked into pasting Terminal commands, which install AMOS, a macOS infostealer that harvests passwords, browser data, and crypto wallet information. The Windows download button was non-functional — only the Mac payload worked.
Defining the MVC: Recover faster from cyberattacks by restoring what matters most
Organizations struggle to recover from cyberattacks not due to missing backups, but from trying to restore everything simultaneously. The Minimum Viable Company (MVC) concept offers a better approach: identifying the minimum people, processes, and technology needed to keep functioning during a crisis. Key recovery capabilities include mapping critical services, establishing a trusted foundational layer, isolating recovery assets, building clean-room recovery environments, and validating plans through realistic rehearsals.
No standing still: Zero Trust and cybersecurity
Cyberattacks are growing in speed and scale, costing businesses billions — recent incidents hit Jaguar Land Rover, WestJet, and Collins Aerospace. With public trust in data handling already low, companies need modernized security strategies. Zero Trust, built on "never trust, always verify," limits breach damage by confining access rather than relying on a single perimeter. Despite 96% of firms planning adoption, only 35% have implemented it, highlighting an urgent need for cross-industry action and consistent standards.

Report: Australia’s transport sector under-prepared for risk of cyber attack
Matched: Australia
A survey of Australia's logistics industry found fewer than half of respondents feel prepared to handle a cyber security incident, highlighting significant vulnerabilities in the transport sector. The findings suggest the industry lacks adequate readiness to defend against or respond to cyber attacks, raising concerns about potential disruptions to critical supply chain infrastructure.
9 in 10 Aussies know property scams exist – but only half can spot one
Matched: Australia
Nine in ten Australians are aware property scams exist, but only half feel confident identifying one, according to new research. The gap between awareness and detection ability has widened, raising concerns about settlement security. Experts warn fraud is becoming increasingly sophisticated, leaving buyers and sellers vulnerable despite general awareness of the risks.
ASD warns Australian TeamCity servers under attack
Matched: Australia
Australia's signals directorate has warned that JetBrains TeamCity servers in the country are being actively exploited following a critical authentication bypass vulnerability. The flaw, which allows attackers to gain administrative control without credentials, was patched in late July. Organisations running unpatched TeamCity instances are urged to update immediately.
SCX.ai partners with DDN after ASX debut
Matched: Australia
SCX.ai has partnered with AI data intelligence firm DDN shortly after listing on the Australian Securities Exchange on 21 August. The partnership follows the company's fully underwritten $40 million IPO debut. The collaboration is expected to strengthen SCX.ai's data and AI capabilities, combining its platform with DDN's infrastructure expertise.
High Alert! ACSC warns of hackers targeting Aussie orgs using TeamCity On-Premises
Matched: Australia
Australia's cyber security agency has warned that hackers are actively exploiting a vulnerability in JetBrains' TeamCity On-Premises software to target Australian organisations. The flaw, roughly a month old, allows attackers to gain unauthorised access to affected networks. The ACSC is urging organisations using the platform to apply available patches immediately to reduce their exposure.
ACSC warns of active exploitation of TeamCity servers in Australia
Matched: Australia
Australia's cyber security agency has issued a high-severity alert warning of active exploitation of a vulnerability in TeamCity On-Premises servers within the country. The ACSC is urging affected organisations to apply patches or mitigations immediately to protect against the ongoing attacks targeting the software.
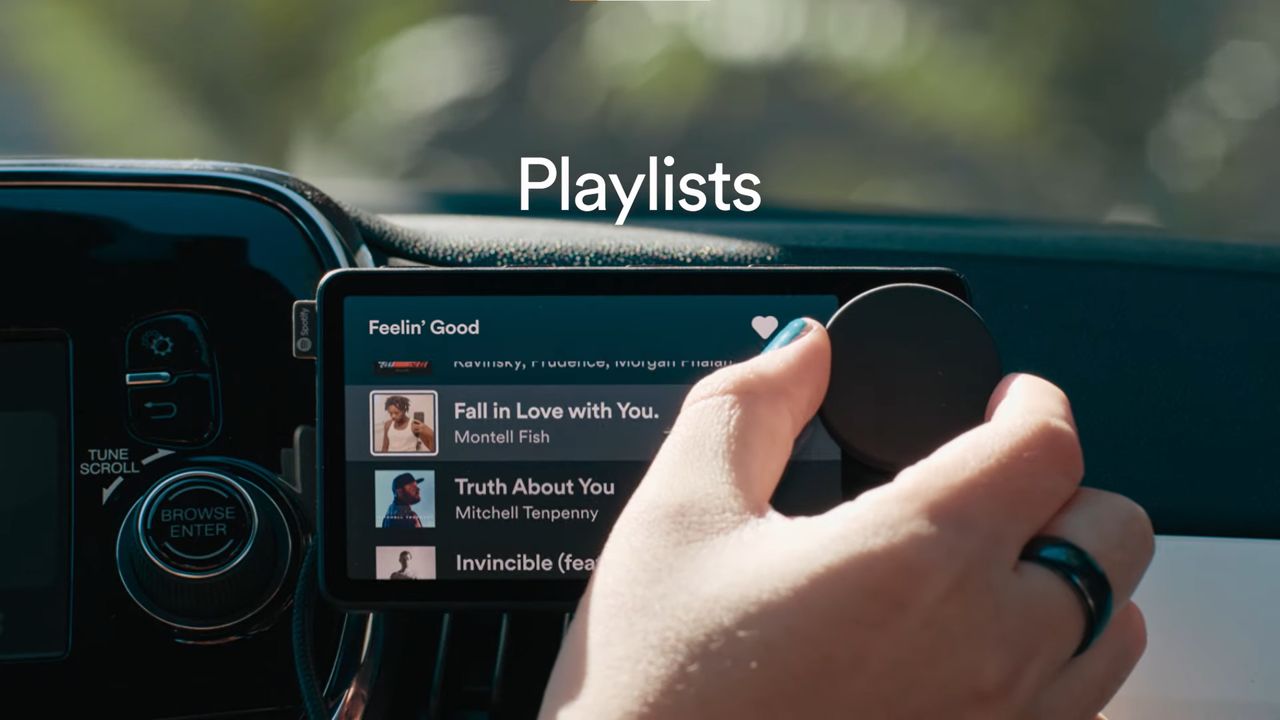
Even connected car head units are being targeted by hackers now — experts warn in-car systems are at risk of being hijacked into a botnet
Kaspersky has identified the first malware campaign built specifically to target Android-based car head units, linking it to the MoYu Group behind the BadBox botnet. Attackers hijacked a legitimate software update channel in DoFun-manufactured devices to silently deliver malware capable of ad fraud, displaying unwanted ads, and harvesting device data. The malware runs invisibly with no user-facing interface. DoFun says the issue has since been resolved on most affected devices.
New malware targets Microsoft Teams users by posing as your company's IT helpdesk
A new backdoor malware called SynkLoader is targeting Microsoft Teams users via fake IT helpdesk messages urging victims to install a malicious "PowerShell Cleaner" hosted on Azure. Key modules include PhishLocker, which displays a fake Windows login screen to steal passwords, and Interactive Shell, enabling full remote control. Organizations are advised to treat unsolicited Teams messages with suspicion and verify requests directly with IT.
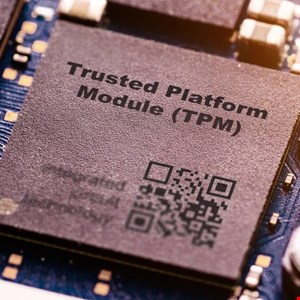
New Guidance Helps Businesses Verify Quantum-Safe Hardware Claims
The Trusted Computing Group has released guidance to help businesses verify whether trusted platform modules genuinely meet quantum-safe security requirements. The move addresses growing concerns that hardware marketed as quantum-resistant may not deliver on those claims, giving organisations clearer tools to assess and confirm the cryptographic capabilities of security hardware as quantum computing threats advance.
NIST Warns of Unique Security Risks in Multi-Cloud Environments
NIST has identified 23 unique security challenges posed by multi-cloud environments, where organizations use services from multiple cloud providers simultaneously. The risks include increased attack surfaces, complex identity management, inconsistent security policies, and difficulties in data governance. NIST is calling on the cybersecurity community to develop solutions to address these emerging threats as multi-cloud adoption continues to grow.
Fake Codex Download Uses Google Sites to Deliver macOS Malware
Attackers created fake codec download pages hosted on Google Sites to distribute macOS malware. The campaign used sponsored search results to drive traffic and employed a ClickFix-style social engineering technique, tricking users into manually running malicious commands. The use of Google's infrastructure helped bypass security warnings and lend the pages false legitimacy.
Canadian SickKids hospital hit again by cyberattacks, more data stolen
Canada's SickKids pediatric hospital suffered a cyberattack exploiting a third-party software vulnerability, exposing personal data of current and former employees and job applicants. Clinical systems and patient records were unaffected. Those impacted are being offered 24 months of free credit monitoring. The hospital was previously hit by LockBit ransomware in late 2022, marking this its latest security incident.
Private equity giant Apollo confirms data breach saw personal info stolen
Apollo Global Management confirmed a cyberattack between July 6–10, 2026, in which a threat actor used social engineering to access its cloud environment. Stolen data included names, dates of birth, contact information, addresses, and Social Security numbers. Financial data was not compromised. Apollo notified authorities, engaged forensic experts, and is offering affected individuals two years of free identity protection. No group has claimed responsibility and the data has not appeared on the dark web.