Cybersecurity News
Filters
Filtered by tag: ransomware × Clear
Boston Scientific says cyberattack is causing a ‘global disruption’ to medical device operations
Matched: health, medical
Boston Scientific confirmed a cyberattack causing global disruptions to IT systems and operations, filing an 8-K with the SEC. The incident has impacted order processing and shipping, with third-party cybersecurity experts brought in to assist. The attack type was not disclosed, though the disruption pattern suggests ransomware. No group has claimed responsibility, and no stolen data has been reported. Full restoration timeline remains unknown.

Nutex Health Data Breach – Hackers Gained Access to Network and Exfiltrated Data
Matched: health
Nutex Health, a Houston-based healthcare company, has disclosed a data breach after an unknown third party accessed and exfiltrated data from its servers. Revealed in an SEC Form 8-K filing dated August 24, 2026, the incident's full scope remains undetermined. Potentially affected data includes patient records, employee information, financial data, and intellectual property. The company activated its response plan, engaged forensic experts, and notified law enforcement.
ShinyHunters hackers claim to have hit data center provider used by Microsoft and Meta
ShinyHunters claims to have breached CyrusOne, a major US data center operator serving Microsoft, Meta, and other large firms, demanding $13 million ransom. The alleged haul includes 12.9 million Salesforce records, 600GB of SharePoint data, employee PII, contracts, and facility diagrams including floor plans and access-control records. CyrusOne has not commented or engaged with attackers. Researchers warn the physical infrastructure data could enable real-world break-ins and sophisticated supply-chain attacks against CyrusOne's customers.
Defining the MVC: Recover faster from cyberattacks by restoring what matters most
Organizations struggle to recover from cyberattacks not due to missing backups, but from trying to restore everything simultaneously. The Minimum Viable Company (MVC) concept offers a better approach: identifying the minimum people, processes, and technology needed to keep functioning during a crisis. Key recovery capabilities include mapping critical services, establishing a trusted foundational layer, isolating recovery assets, building clean-room recovery environments, and validating plans through realistic rehearsals.
Canadian SickKids hospital hit again by cyberattacks, more data stolen
Canada's SickKids pediatric hospital suffered a cyberattack exploiting a third-party software vulnerability, exposing personal data of current and former employees and job applicants. Clinical systems and patient records were unaffected. Those impacted are being offered 24 months of free credit monitoring. The hospital was previously hit by LockBit ransomware in late 2022, marking this its latest security incident.
The ascent of autonomous attacks and the race to contain them
AI is enabling autonomous cyberattacks that can conduct reconnaissance, breach systems, and adapt without human input. A 2025 Jaguar Land Rover attack cost £485m in losses. Smaller businesses face growing exposure as AI scans for vulnerabilities at scale. Defenses need to shift toward continuous monitoring, strong identity controls, and AI-powered detection, supported by human expertise, to counter threats moving faster than traditional security measures.
Scammers pose as ransomware recovery agents, but just go on to steal more from victims
Cybercriminals are posing as ransomware recovery specialists to defraud victims twice. Groups like "Ransom Busters" pose as legitimate recovery firms, approach ransomware victims, and pocket fees without delivering results. In reality, they are ransomware affiliates exploiting desperate victims. Experts warn organizations to thoroughly vet any recovery service before paying, as the fake recovery industry is growing alongside ransomware itself.
Exclusive: Ransomware newcomers list South Australia’s Ramsey Bros as hacking victim
Matched: Australia
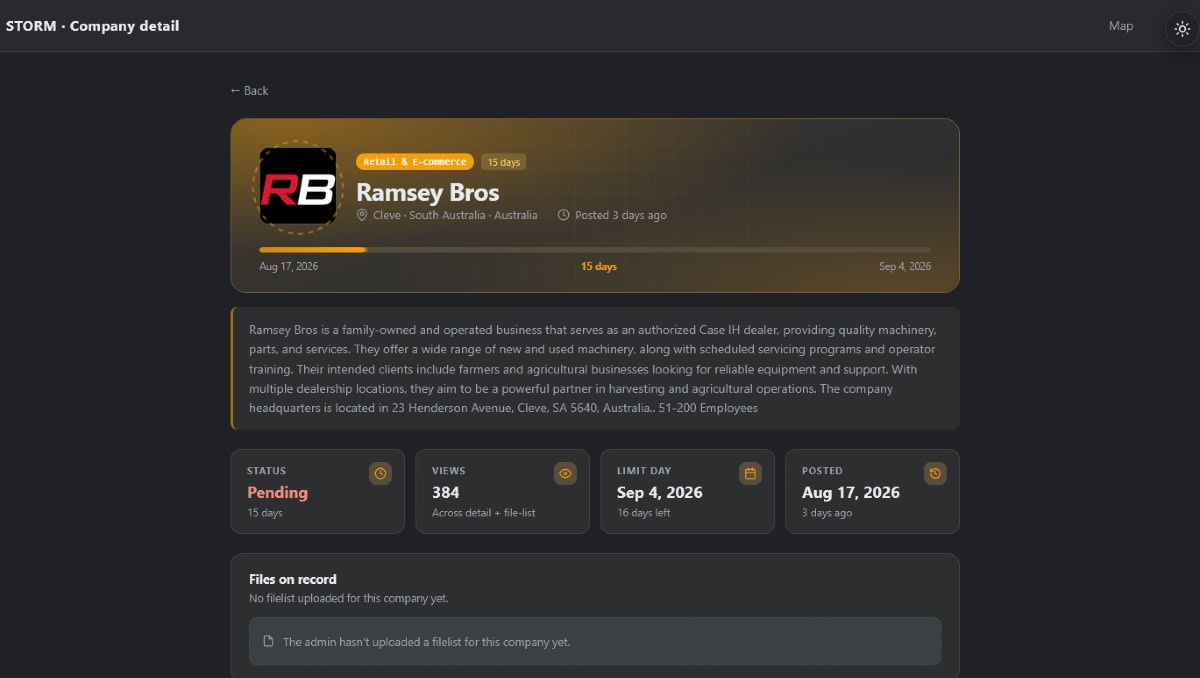
Ransomware group Storm claims to have hacked Ramsey Bros, a South Australian farm machinery supplier. The group says it has published stolen data as proof, including alleged customer information and vehicle inspection records. Ramsey Bros has not yet publicly commented. Storm is considered a newcomer among ransomware groups, which typically steal and threaten to leak data to pressure victims into paying.

CISA Warns Medusa Ransomware Hackers Steal Data, Kill Security Tools, and Encrypt Entire Networks
Matched: health
CISA, the FBI, and HHS have jointly issued an updated advisory warning that Medusa ransomware attackers are actively targeting enterprise networks, disabling security tools, stealing sensitive data, and encrypting entire systems. The alert urges organizations to strengthen defenses against the group, which has escalated its activity across critical sectors.
Thousands of Hacked WordPress Sites, One Operation: Unmasking StopAndProtect
Researchers at Check Point identified a ransomware operation called StopAndProtect in May 2026. The campaign uses the ClickFix social-engineering technique to trick victims into running a PowerShell command, triggering a multi-stage downloader chain. Thousands of hacked WordPress sites serve as infrastructure for the operation, which researchers have now partially unmasked through analysis of its infection chain and supporting infrastructure.
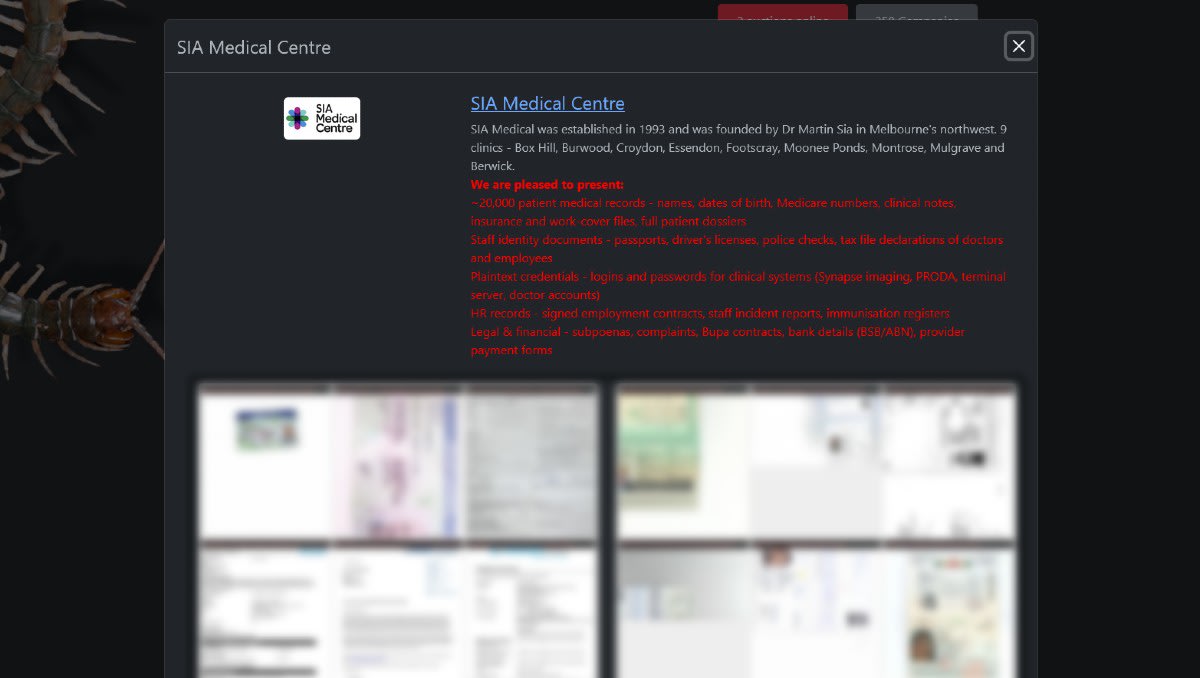
Exclusive: SIA Medical Centre confirms it is investigating cyber incident involving patient data
Matched: medical
Victorian medical centre SIA Medical Centre is investigating a ransomware attack after the Rhysida cyber extortion group claimed to have obtained thousands of patient records. The centre confirmed it is responding to a cyber incident involving patient data. Rhysida, a known ransomware group, has listed the stolen data and is threatening to release it unless a ransom is paid.
Ransomware gang crashes own attack — with no-one to blame but themselves
Ransomware group Akira accidentally sabotaged its own attack after using a driver exploit to disable endpoint detection software — the same technique also killed their encryption tool. Researchers noted the self-inflicted failure but warned the tactic of using vulnerable drivers to bypass security is increasingly common and remains a serious threat even when, as here, it backfires on the attackers.
17th August – Threat Intelligence Report
Colombia's Ministry of Justice suffered a ransomware attack disrupting technology infrastructure and public services tied to drug monitoring and legal processes, with officials confirming file compromise. Other notable incidents include additional breaches and cyberattacks detailed in Check Point Research's weekly Threat Intelligence Bulletin, covering top attacks, emerging vulnerabilities, and threat actor activity for the week of 17th August.
Exclusive: Australian truck trailer company Midland among dozens of victims listed by Cl0p cyber extortion group
Matched: Australia
Ransomware group Cl0p has listed over 40 victims in a single day, including major companies such as Philips, General Electric, Tristar, Shell, and Australian truck trailer manufacturer Midland. The prolific cyber extortion gang typically publishes victim details when ransom demands go unpaid, using the threat of data exposure as leverage.
Akira Hits Safe Mode: Ransomware Rebooting Around EDR
An Akira ransomware affiliate attempted to bypass endpoint detection by rebooting a victim's system into Safe Mode, which prevents most security tools from loading. The tactic backfired when Safe Mode also blocked their own ransomware from executing properly. Researchers documented the full attack chain, highlighting how threat actors are adapting techniques against modern EDR solutions, sometimes with self-defeating results.
One in three ANZ organisations still pay ransomware demands, Commvault research says
Matched: Australia
One in three organisations in Australia and New Zealand still pay ransomware demands, according to Commvault research, despite uncertainty about whether data will be recovered or operations restored. The findings highlight ongoing vulnerabilities and suggest many organisations lack confidence in their ability to recover without meeting attackers' demands.

Gunra Ransomware Exploits Fortinet and Schneider Electric Flaws to Breach Networks
Matched: health
South Korean and US cybersecurity agencies have warned about Gunra ransomware targeting critical infrastructure globally, including healthcare, financial services, government, and nonprofit sectors. The attacks exploit vulnerabilities in Fortinet and Schneider Electric systems. Gunra follows a ransomware-as-a-service model and represents a continuing trend of sophisticated ransomware variants threatening essential services worldwide.
Exclusive: Kairos ransomware lists Warwick Fabrics NZ as hack victim
Matched: medical
New Zealand textile company Warwick Fabrics has been listed as a victim by the Kairos ransomware group, which claims to have stolen 386 gigabytes of data. The alleged breach includes sensitive employee information such as passports, medical reports, and salary data. The company has not yet publicly responded to the claims.

Russian Hacker Breaches Companies, Sells Their Access and Spies on Ukrainian Military Sites
Matched: health
A Russian-speaking hacker has been linked to a broad campaign breaching organizations across multiple sectors worldwide, including education, healthcare, finance, and government. The actor exploited exposed security appliances and public applications to harvest credentials and sell network access to ransomware groups. The operation also reportedly included surveillance activity targeting Ukrainian military websites.
Exclusive: Partnered Health responds to Inc Ransom data breach claims
Matched: Australia, health
Australian GP network Partnered Health is responding to claims by cyber extortion group Inc Ransom, which alleges it stole terabytes of data from the organisation. At least 21 clinics may be affected. Partnered Health has not confirmed the breach but is investigating. Inc Ransom typically publishes stolen data if ransom demands go unmet.